
FortiAnalyzer 300G in Uganda
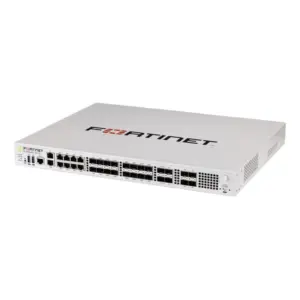
A 1U centralized log and analysis appliance for security teams that need consolidated visibility, investigation workflows, reporting, and scalable retention across Fortinet Security Fabric environments.
The 300G is positioned for organizations whose log volumes and device counts have moved beyond entry-level analytics but do not require the capacity of Fortinet’s larger FortiAnalyzer appliances. Its key sizing variables are daily ingest, sustained logs per second, retention expectations, device or VDOM count, and the security services selected for the deployment.
Fortinet
FAZ-300G
Centralized log & analysis appliance
Up to 100 GB/day
1 RU rackmount
Quote & availability on request
A practical middle tier for centralized security telemetry
FortiAnalyzer 300G is a dedicated hardware platform for organizations that want a central place to ingest, normalize, retain, search, correlate, and report on security and network logs. Rather than asking administrators to examine individual FortiGate units or separate consoles, FortiAnalyzer consolidates data into a unified operational view. That makes the appliance relevant to security teams that need consistent visibility across branch networks, headquarters infrastructure, user activity, incidents, and policy events.
Its published capacity profile places it between the smaller 150G and larger models such as the 810G. Fortinet specifies up to 100 GB of logs per day, a sustained analytic processing rate of 2,000 logs per second, and a Collector-mode sustained rate of 3,000 logs per second. It supports up to 180 devices or virtual domains and up to 25 Administrative Domains, giving organizations room to separate environments, business units, customers, or administrative boundaries where that structure is required.
The hardware configuration is also important. The appliance ships with 8 TB of storage built from two 4 TB drives. With the default RAID 1 arrangement, usable storage is 4 TB. RAID 0 and RAID 1 are supported, and RAID is software-based on this model. The appliance is a 1 RU rackmount system with four Gigabit Ethernet RJ45 interfaces. These details matter because they define not only rack and network planning, but also how an organization should think about retention, resiliency, and future scaling.
FortiAnalyzer capabilities extend beyond simple log archiving. Fortinet positions the platform as a unified security operations system with analytics and correlation, threat intelligence integrations, event handling, automation, reporting, and integrations across the Security Fabric. Optional services can add features such as IOC and outbreak detection, SOC automation, OT-focused analytics, security rating and compliance functions, threat intelligence platform capabilities, FortiAI assistance, and SOC monitoring services. Buyers should therefore define both the hardware requirement and the service outcome they expect before finalizing an order.
For Uganda organizations, FourTeck can assist with model validation, appliance-versus-virtual discussions, bundle selection, expected log-volume sizing, and quote preparation. The right decision is usually based on measured or estimated ingest rather than simply counting firewalls. A small number of busy gateways can create more logs than a larger number of lightly used branch devices, so estimating average and peak rates is central to a reliable purchase.
Operational value for security and infrastructure teams
Consolidated security evidence
A central data lake reduces the fragmentation that occurs when logs stay distributed across multiple appliances. Administrators can investigate activity from one platform, compare events across devices, and build reports without repeatedly signing into separate systems. The business value is faster diagnosis and a more consistent record of security activity for operations, audit, troubleshooting, and management reporting.
Capacity matched to a growing SOC
The published 100 GB/day ingest and 2,000 sustained analytic LPS give buyers a concrete sizing envelope. This is especially useful for organizations moving from basic device-level logging toward formal monitoring and incident workflows. The value is predictability: teams can map measured log generation to a specific appliance class before committing budget.
More efficient investigation
FortiAnalyzer combines log search, correlation, dashboards, reports, threat context, and incident-oriented capabilities. Security analysts can move from a detected event into related telemetry without rebuilding the investigation manually across every device. That can reduce time spent locating evidence and improve the consistency of incident review.
Structured administrative separation
Support for up to 25 ADOMs helps environments that need logical separation between business units, administrative teams, customers, or managed segments. Proper ADOM planning can simplify delegated administration and reporting while keeping the platform centralized.
Deployment flexibility within the Fortinet ecosystem
FortiAnalyzer can operate in Analyzer or Collector roles, and Fortinet also supports broader FortiAnalyzer Fabric architectures. This gives organizations a path to distribute log collection or scale operational design as environments expand, rather than treating every appliance as an isolated logging island.
Optional services tied to defined security outcomes
Organizations can select additional services for IOC analysis, outbreak detection, automation, OT security, threat intelligence, AI assistance, and other workflows. This lets procurement separate the base hardware decision from the security-service scope, which is useful for phased projects and budget planning.
Designed around centralized evidence, measurable ingest, and Security Fabric context.
What distinguishes this model is not a single headline feature but a balanced capacity profile for organizations that need a dedicated appliance with meaningful storage and processing headroom. The 300G can collect and analyze telemetry at a scale that suits many mid-sized and distributed environments while remaining compact enough for a standard 1U rack footprint.
Provides a clear daily log-volume ceiling for sizing.
Supports sustained analysis workloads within the published rating.
Suitable for consolidated monitoring across substantial distributed estates.
Two 4 TB drives with 4 TB usable under the default RAID 1 configuration.
FortiAnalyzer 300G specifications
| Specification | Published value | Buyer significance |
|---|---|---|
| Product SKU | FAZ-300G | Use for exact model validation and quotation. |
| Daily log capacity | 100 GB/day | Primary ingest-sizing metric. |
| Analytic sustained rate | 2,000 logs/sec | Important for continuous analysis workloads. |
| Collector sustained rate | 3,000 logs/sec | Relevant when deployed primarily as a Collector. |
| Devices / VDOMs | Up to 180 | Check against current and planned managed estate. |
| Maximum ADOMs | 25 | Matters for administrative or tenant segmentation. |
| Maximum analytics days | 50 days at maximum sustained analytic rate | Actual retention can be longer at lower average rates. |
| Interfaces | 4 × RJ45 Gigabit Ethernet | Plan management and log network connectivity. |
| Installed storage | 8 TB (2 × 4 TB) | Physical storage before RAID overhead. |
| Usable storage | 4 TB after default RAID | Important for retention planning. |
| RAID | RAID 0/1; software RAID; default RAID 1 | Default design favors mirrored storage resiliency. |
| Form factor | 1 RU rackmount | Reserve one rack unit and suitable airflow. |
| Dimensions | 4.4 × 43.8 × 41.6 cm | Verify cabinet depth and service clearance. |
| Weight | 10.2 kg | Useful for rack and installation planning. |
| AC input | 100–240 V AC, 50–60 Hz | Confirm datacenter power provision and UPS design. |
| Power consumption | 90.1 W average / 99 W maximum | Supports power and cooling estimates. |
| Operating temperature | 0°C to 40°C | Maintain rack environment within published range. |
| Optional redundant PSU | Available option | Consider where power-path resilience is required. |
The most important specifications are the ones that describe sustained data flow and how long the organization expects to retain searchable analytics. Daily gigabytes alone can hide short peaks, while device count alone does not describe how noisy those devices are. A useful sizing exercise therefore combines average daily ingest, sustained and peak log rates, desired retention, and growth assumptions. The published 50-day analytics figure is based on continuous logging at the maximum sustained analytic rate; a lighter real-world rate can increase the number of days retained.
Storage design is the next decision point. The default RAID 1 configuration leaves 4 TB usable from the two installed 4 TB drives and protects against a single-drive failure by mirroring data. Organizations that have unusually long retention requirements should examine whether the 300G’s local storage profile remains appropriate or whether a larger appliance, distributed architecture, or other retention strategy is preferable. Network teams should also account for four 1GbE RJ45 interfaces, rack depth, airflow from front to back, and optional power redundancy when planning the physical installation.
Five questions to answer before ordering
01 — What workload must the appliance absorb?
Estimate the current daily log volume and the sustained logs-per-second rate generated by your environment. Include FortiGate traffic and event logging as well as other supported Fortinet or third-party sources you expect to onboard. This determines whether the 100 GB/day and 2,000 analytic LPS envelope is comfortable or too close to the expected operating ceiling.
02 — How many devices, VDOMs, and administrative boundaries are required?
The 300G supports up to 180 devices or VDOMs and up to 25 ADOMs. Count existing infrastructure, planned branch additions, virtual domains, and any administrative separation needed for departments or managed environments. Growth should be included rather than sizing only for today’s estate.
03 — What must integrate with the platform?
Confirm FortiGate versions, Security Fabric components, third-party log sources, ticketing or notification workflows, and any reporting or compliance processes. Integration requirements can influence configuration, software version planning, service selection, and whether FortiAnalyzer is expected to act primarily as an analyzer, a collector, or part of a broader architecture.
04 — Which services and future capabilities matter?
Optional services include FortiGuard IOC and outbreak detection, SOC automation, OT security functions, security rating and compliance services, FortiGuard Threat Intel Platform capabilities, FortiAI, and SOCaaS monitoring. Select services according to operational requirements rather than assuming every deployment needs the same bundle.
05 — What are the infrastructure and support expectations?
Review rack space, AC power, UPS capacity, airflow, optional redundant power supply requirements, support term, project timeline, quantity, and delivery destination. These details affect the final bill of materials and quotation even when the appliance model itself is already selected.
Quote Preparation
Share your expected GB/day, average and peak LPS, device/VDOM count, target retention, ADOM count, required FortiGuard or automation services, preferred support term, rack/power requirements, delivery city, and project quantity. This gives FourTeck enough context to review whether FAZ-300G is the right fit and prepare a more useful quotation.
Where the 300G can make operational sense
Multi-site enterprise security monitoring
An organization with headquarters and a growing branch estate may need to bring FortiGate and other Security Fabric logs into a single operational view. The 300G can fit when aggregate ingest remains within its 100 GB/day sizing range and the total estate stays within the supported device or VDOM maximum. The buyer should verify peak LPS because branch traffic patterns can create bursts even when daily log volume looks moderate.
Institutional audit and troubleshooting
Universities, large schools, healthcare organizations, NGOs, and similar institutions often need more than live firewall dashboards. Centralized historical logs can support policy review, incident investigation, troubleshooting, and evidence collection. The important configuration point is retention: if the institution needs a long historical window, daily ingest and usable RAID storage must be modeled together before purchase.
Growing in-house security operations
A security team formalizing incident monitoring can use FortiAnalyzer to combine dashboards, correlation, reports, event handlers, and optional automation. The 300G provides a dedicated hardware foundation without moving immediately to higher-capacity models. Service subscriptions should be selected according to the workflows the team will actually operate.
Segmented or managed environments
Support for up to 25 ADOMs can be useful where teams need separated administrative contexts, such as business units, customer environments, or operational domains. The architecture should be planned carefully because ADOMs, device counts, logging rates, and delegation requirements all influence whether a single appliance remains the best topology.
Log-rate sizing is the purchase decision that deserves the most attention
Security analytics platforms are often compared by storage or device count first, but sustained log rate can be the more revealing metric. A device estate is not uniform: two sites with the same number of FortiGate appliances can produce dramatically different event volumes because of user count, policies, traffic patterns, enabled logging, security services, and application activity. The 300G’s published 2,000 logs-per-second sustained analytic rate gives a concrete boundary for sizing analysis workloads, while Collector mode raises the sustained receiving rate to 3,000 logs per second when the appliance’s primary role is forwarding and archiving logs.
For procurement teams, this means a reliable quote request should include more than a simple statement such as “we have 40 firewalls.” Ask the technical team for recent log-volume measurements, average and peak rates, and whether future systems will be onboarded. If exact measurements are unavailable, build a conservative estimate and leave room for growth. The goal is to avoid operating permanently close to a platform’s maximum published rate, because new branches, additional logging, incident bursts, or richer telemetry can consume headroom.
Fortinet also publishes a maximum of 50 analytics days at the maximum sustained rate for this model. That figure can increase when actual rates are lower, but it should be treated as a planning reference rather than a universal guarantee. Organizations with strict retention requirements should model the intended data volume carefully and consider how archive policy, reporting needs, and investigations interact with storage.
From raw events to usable security context
Centralized logging becomes valuable when teams can transform collected events into investigation and response workflows. FortiAnalyzer is built around this transition: it aggregates telemetry, correlates activity, enriches investigations with threat intelligence, and supports reporting and automation. In a Fortinet Security Fabric environment, that can create a more coherent view of what happened across network, endpoint, identity, application, and cloud-related signals supported by the platform.
The operational benefit is not simply having “more logs.” Analysts need to reduce the time spent searching multiple consoles, reconstructing timelines, and manually passing information between tools. FortiAnalyzer’s event handlers, content packs, playbooks, reports, and optional services provide a foundation for more repeatable workflows. Organizations can start with centralized analytics and expand the workflow depth as the SOC matures.
Unified data handling: centralize supported logs and telemetry for cross-environment visibility.
Threat-oriented analysis: combine correlation, indicators, outbreak intelligence, and incident context according to licensed capabilities.
Workflow automation: use event handlers, connectors, playbooks, reporting, and optional automation services to reduce repetitive analyst work.
Storage, RAID, and physical deployment should be reviewed as one decision
The 300G includes 8 TB of installed storage across two 4 TB drives. With the default RAID 1 configuration, usable capacity is 4 TB because data is mirrored. RAID 0 is also supported, but a buyer should not treat those options as interchangeable. RAID 1 reduces usable space but provides drive-level redundancy; RAID 0 emphasizes capacity and performance without mirroring. The correct choice depends on the organization’s resilience and retention priorities.
The physical appliance occupies one rack unit, measures approximately 4.4 × 43.8 × 41.6 cm, weighs 10.2 kg, and uses front-to-back airflow. Average published consumption is 90.1 W with a 99 W maximum, and an optional redundant hot-swap power supply is available. These are relatively straightforward datacenter requirements, but they still need to be checked against cabinet depth, PDU capacity, UPS design, cooling, and cable management.
Buyer decision checklist
☐ Confirm whether default RAID 1 aligns with retention and resilience requirements.
☐ Verify rack depth, one available RU, airflow direction, and installation access.
☐ Confirm the four 1GbE RJ45 interfaces fit the planned network design.
☐ Decide whether optional redundant power is required.
☐ Size UPS capacity and power distribution for the appliance and related network equipment.
☐ Validate retention targets against measured ingest rather than raw disk capacity alone.
What buyers should check before purchase
| Risk | What to confirm | Why it matters | What to share with FourTeck |
|---|---|---|---|
| Undersized ingest | Average and peak log volume | A device count can hide heavy logging | GB/day and LPS estimates |
| Insufficient retention | Required searchable days/months | Retention depends on ingest and usable storage | Policy or compliance target |
| Wrong service bundle | IOC, automation, OT, AI, SOCaaS needs | Capabilities and renewals vary by selected service | Required operational functions and term |
| Infrastructure mismatch | Rack, power, UPS, cooling, cabling | Deployment can be delayed by overlooked physical constraints | Rack and power environment |
A procurement team should also verify the exact model code on the quotation, the selected support period, compatibility with the intended FortiAnalyzer software release, and any accessories needed for the rack or power design. If this appliance is replacing an older FortiAnalyzer, include migration expectations and current configuration details. If it will join an existing FortiAnalyzer architecture, describe the planned Analyzer, Collector, or Fabric role. Project quantity and delivery location should be stated early because availability can vary and larger deployments may require phased coordination.
Procurement support for Uganda projects
FortiAnalyzer 300G availability in Uganda can vary by timing, selected bundle, support term, and project quantity. FourTeck can help buyers review the required appliance and associated services, prepare a quotation, and coordinate supply planning without assuming that every configuration is held locally. For security infrastructure projects, it is useful to request the quote early enough to validate license terms, accessories, and delivery requirements before installation dates are fixed.
For Kampala-based deployments, the discussion can include rack environment, network interfaces, log-volume sizing, and whether the appliance will be used as the main Analyzer or as part of a broader design. FourTeck can also help interpret when a larger FortiAnalyzer model or a virtual/cloud approach may be more appropriate based on the technical requirement. Warranty and support guidance should be tied to the exact quoted SKU and service package rather than assumed from the base hardware name alone.
Organizations preparing a multi-unit or project purchase should share target quantities, delivery schedule, support duration, and any required FortiGuard or automation services. This gives the quotation process enough context to distinguish the base appliance from a bundled security-operations solution.
Uganda location coverage
FourTeck can coordinate product enquiries and quotation support for organizations planning deployments in Kampala, Entebbe, Jinja, Mbarara, and Gulu, as well as other locations in Uganda. Delivery feasibility and timing depend on the specific order, quantity, service bundle, and current supply conditions, so buyers should request confirmation for the exact project rather than relying on a general stock assumption.
East Africa and regional sourcing
Organizations operating across several countries may prefer to standardize Fortinet security operations around a consistent appliance and service policy. FourTeck can discuss requirements for Uganda and, where relevant to the project, coordinate enquiries across Kenya and selected East Africa or Africa markets. Regional projects should define where equipment will be installed, which entity is purchasing, required support terms, and whether configurations must be identical across sites.
For buyers with procurement links to the UAE or Kuwait, FourTeck’s regional sites can also provide a starting point for those market enquiries. Cross-border availability, commercial terms, logistics, taxes, and warranty handling vary by country and transaction, so they should be confirmed per quotation. The practical objective is consistency: model, service bundle, software planning, and deployment responsibilities should be clearly documented for every location.
Regional links: FourTeck Uganda, FourTeck Kenya, FourTeck Africa, FourTeck UAE, and FourTeck Kuwait.
Related Fortinet and security infrastructure options
Practical assistance before the purchase order
01. Product selection guidance. Buyers can share log volume, device count, retention, and growth expectations so the discussion starts from workload rather than model familiarity alone.
02. Configuration review. FourTeck can help separate the base appliance requirement from optional services, support terms, and infrastructure considerations that affect the final bill of materials.
03. Quote preparation. A structured quote can reflect the correct model, requested service duration, project quantity, and destination rather than presenting a generic hardware-only figure.
04. Business IT context. Security analytics is connected to firewalls, switching, WAN design, server infrastructure, power, and operational processes. Reviewing the surrounding environment can uncover compatibility or capacity issues before deployment.
05. Uganda delivery coordination. Delivery planning can be discussed against the actual project city, quantity, and timeline. Availability should be confirmed per quotation.
06. Alternative path review. If 300G capacity is too small or unnecessarily large, buyers can compare another FortiAnalyzer appliance or a VM/cloud deployment approach before locking the architecture.
FortiAnalyzer 300G buyer questions
01. What is FortiAnalyzer 300G mainly used for?
It is a dedicated centralized log and analysis appliance for security operations. Organizations use it to consolidate supported logs and telemetry, search historical events, create reports, correlate activity, investigate incidents, and support automated workflows. It is particularly relevant in Fortinet Security Fabric environments where teams want a central operational view rather than checking each security device independently.
02. How much logging can the 300G handle?
Fortinet publishes a capacity of up to 100 GB of logs per day, a sustained analytic rate of 2,000 logs per second, and a Collector-mode sustained rate of 3,000 logs per second. Buyers should compare both daily volume and sustained/peak LPS against measured or estimated traffic because either can become the limiting factor in a busy environment.
03. How many Fortinet devices can it manage for logging and analytics?
The model supports up to 180 devices or VDOMs and up to 25 ADOMs according to Fortinet’s published specifications. The practical fit still depends on how much telemetry those devices generate. A smaller number of heavily used gateways can generate more logs than a larger fleet of light branch devices, so device count should never be the only sizing measure.
04. What storage is included?
The appliance includes 8 TB of installed storage using two 4 TB drives. Under the default RAID 1 configuration, usable storage is 4 TB because the drives are mirrored. The model supports RAID 0 and RAID 1 using software RAID. Retention planning should use expected ingest and the desired analytics window, not simply the raw 8 TB figure.
05. Are FortiGuard and automation services included automatically?
Not every optional service should be assumed to be included with a base hardware quote. Fortinet offers services such as IOC and outbreak detection, SOC automation, OT security, security rating and compliance, threat intelligence platform capabilities, FortiAI, and SOCaaS. The exact bundle and term need to be selected and quoted according to the required operational features.
06. Can the 300G be used as a Collector?
Yes. FortiAnalyzer supports Analyzer and Collector operational modes. In Collector mode, the system focuses on receiving, forwarding, and archiving logs so that analysis workloads can be handled elsewhere in a distributed design. Fortinet publishes a 3,000 logs-per-second sustained Collector rate for the 300G. The correct architecture depends on total ingest and the broader FortiAnalyzer topology.
07. Does it support redundant power?
Fortinet lists redundant hot-swap power supplies as an optional capability for the 300G. If the appliance will support an important security operations function, buyers should decide whether power-path redundancy is required and confirm the exact power-supply configuration on the quotation. UPS capacity, PDU design, and rack power availability should be checked at the same time.
08. Is FortiAnalyzer 300G available in Uganda?
FourTeck can provide quotation and availability guidance for Uganda projects, but availability can vary by date, bundle, support term, and quantity. Buyers should request confirmation for the exact SKU and project rather than assume local stock. Providing the destination, required services, and target deployment schedule helps FourTeck prepare a more accurate supply discussion.
09. What information should I send for a quote?
Send the expected daily log volume, average and peak LPS, number of devices or VDOMs, target retention period, ADOM requirement, desired service subscriptions, support term, project quantity, and delivery location. If the system is replacing an older FortiAnalyzer, include that model and current workload. These details help determine whether 300G capacity and the proposed bundle are suitable.
10. When should I consider a larger FortiAnalyzer model?
Consider a larger model when expected ingest, sustained LPS, device or VDOM count, retention needs, interface requirements, or growth plans approach the 300G limits. The 810G and higher models provide progressively greater capacity. A sizing review is preferable to purchasing purely for current usage, especially when new sites, richer logging, or additional security products are planned.
Prepare the right FortiAnalyzer configuration before you request approval
Send FourTeck your daily log estimate, peak LPS, device or VDOM count, required retention, service subscriptions, support term, quantity, and Uganda delivery location. The team can use those details to review the model fit and prepare a project quotation.
Useful details: GB/day • LPS • devices/VDOMs • ADOMs • retention • services • support term • quantity • destination

Reviews
There are no reviews yet.