
Fortinet FortiDDoS 200F DDoS Protection Appliance for Uganda
Fortinet FortiDDoS 200F is a purpose-built inline appliance for protecting Internet-facing networks, applications and services against distributed denial-of-service attacks. It is positioned for organizations that need dedicated mitigation capacity at the network edge, with inspected mitigation rated up to 8 Gbps and 9 million packets per second, more than 4 million TCP sessions, over 2 million DNS/NTP responses per second and a stated time to mitigation below one second. In practical procurement terms, the 200F sits between basic perimeter controls and larger carrier-scale mitigation platforms: it gives enterprises a dedicated enforcement point that continuously observes traffic behavior and can respond automatically when abnormal floods, protocol abuse or application-oriented denial-of-service activity threatens availability.
The appliance is particularly relevant where uptime has a direct operational or financial consequence. Banks may need continuous access to digital banking and payment services; universities may need stable learning, registration and research portals; public-sector organizations may need citizen-facing systems to remain reachable; and commercial enterprises may need customer portals, VPN entry points, DNS infrastructure, APIs and business applications protected from disruption. FortiDDoS is designed around autonomous mitigation, full packet inspection and rapid response, reducing dependence on manual intervention during an attack. This matters because a volumetric or high-packet-rate event can develop faster than a conventional escalation process can react.
For Uganda deployments, procurement should begin with the actual traffic profile rather than nominal Internet bandwidth alone. Circuit speed, normal peak traffic, packet-per-second behavior, protocol mix, protected public address space, expected growth, redundancy topology and interface media all influence whether the 200F is the correct model. FourTeck can help convert these inputs into a practical bill of materials, including the appliance, support coverage, reputation services where required, compatible optics or cabling, rack requirements and implementation planning. The objective is to avoid both under-sizing and unnecessary over-provisioning.
Instant Specifications & Procurement Fact Rail
FortiDDoS 200F / FDD-200F
Up to 8 Gbps / 9 Mpps
1U rack appliance
Dual redundant AC supplies
480 GB SSD
Confirm current availability and lead time
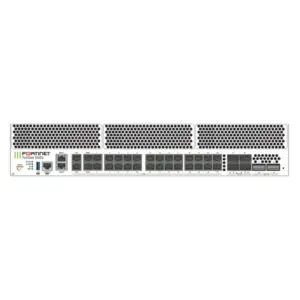
The 200F provides eight DDoS defence port-pairs: four pairs of Gigabit Ethernet RJ45 with integral bypass protection, two pairs of Gigabit Ethernet LC short-reach multimode 850 nm interfaces with integral optical bypass protection, and two pairs of Gigabit Ethernet SFP interfaces without bypass protection. Two additional Gigabit Ethernet RJ45 management ports support administration. This interface mix is an important purchasing detail because the production network path must match the selected copper or optical handoff. Buyers should verify existing switch and router media, fiber type, patching, connector standards and desired bypass behavior before the purchase order is finalized. Regional warranty and support entitlement should likewise be confirmed against the chosen Fortinet support term rather than assumed from hardware supply alone.
Operational Product Architecture & Overview
DDoS protection is fundamentally a traffic-engineering problem as well as a security problem. A device must distinguish legitimate bursts from hostile floods while processing traffic quickly enough that the protective control does not itself become the bottleneck. FortiDDoS 200F is designed as an inline mitigation appliance. Traffic traverses a defence port-pair, allowing the system to inspect flows and enforce mitigation before malicious traffic reaches downstream firewalls, load balancers, application servers or other protected infrastructure. The platform continuously builds behavioral understanding of network traffic and applies mitigation when activity exceeds learned or configured expectations.
The 8 Gbps inspected rate should be read together with the 9 Mpps packet-processing figure. A denial-of-service event may consist of very small packets, so raw gigabit capacity alone can hide a packet-rate limitation. Procurement teams should therefore request both bandwidth and packet-per-second information from network operations. A 2 Gbps Internet service experiencing a tiny-packet flood can impose a very different processing burden from a 2 Gbps stream of large packets. The 200F’s packet-rate specification is therefore central to sizing, not a secondary number.
The appliance also supports more than four million TCP sessions. Session scale matters for public web systems, portals, API gateways and other services where legitimate users can create large numbers of concurrent connections. DDoS events may attempt to exhaust connection state through SYN floods or other TCP behaviors. Dedicated mitigation allows abnormal connection patterns to be identified and constrained before they consume downstream resources. For DNS and NTP, the platform is specified for more than two million responses per second, addressing protocols frequently involved in direct and reflected denial-of-service activity.
FortiDDoS also supports mitigation for modern protocols and attack patterns including advanced DNS and NTP, DTLS and QUIC. This is relevant as Internet application stacks evolve beyond traditional TCP-only assumptions. QUIC, for example, uses UDP as its transport foundation, changing traffic characteristics for modern web services. A procurement plan should account for the protocols actually used by public applications rather than selecting controls based only on historical traffic profiles.
Physical continuity is addressed through integral bypass on specified copper and optical interfaces. Bypass is valuable because an inline device sits directly in the production path. Depending on the chosen port-pair, bypass capability can allow traffic continuity under defined appliance failure conditions. This does not eliminate the need for resilient network design, but it gives architects another mechanism for avoiding a single physical failure becoming a total outage. The dual redundant AC power supplies similarly support connection to independent rack power feeds where the facility provides A/B power.
The 480 GB SSD provides local storage within the appliance. Operational teams should still define how logs, alerts, reports and incident records are retained in the wider monitoring architecture. During procurement, clarify whether local reporting is sufficient for the organization’s audit needs or whether integration with centralized logging, event management or security operations workflows is required. The hardware decision is only one part of a complete DDoS operating model.
Enterprise Business Outcomes & Value Analysis
1. Performance & Throughput Integrity
The 200F is designed to inspect traffic at up to 8 Gbps and 9 Mpps. This gives network architects two dimensions for capacity planning. The practical outcome is a dedicated mitigation layer sized around both bandwidth and packet rate, helping protect downstream infrastructure from floods that could otherwise consume firewall, server or application capacity. Correct sizing should include normal peaks, expected attack exposure and growth headroom.
2. System Reliability & High Availability
Dual redundant AC power supplies, supported high-availability designs and bypass-capable defence interfaces contribute to continuity planning. In a properly engineered deployment, the organization can reduce dependence on a single power feed or appliance path. Buyers should still validate the exact HA topology, switch design, routing behavior and failure sequence before implementation.
3. Network & Infrastructure Scalability
The model is suitable where current inspected traffic fits comfortably within its published limits. Growth planning should account for new Internet circuits, cloud connectivity, public applications and merger or branch consolidation projects. If expected traffic approaches the platform ceiling, a larger FortiDDoS model may provide more useful lifecycle headroom.
4. Enterprise Security & Access Protection
DDoS mitigation complements rather than replaces firewalling, application security and identity controls. Its specific business role is preserving availability when hostile traffic attempts to overwhelm network or service resources. This separation of duties can keep perimeter firewalls focused on policy enforcement while a dedicated platform handles denial-of-service behavior.
5. Centralized Operational Simplicity
Autonomous mitigation reduces the need for an administrator to recognize and manually block every attack pattern during an incident. Operational teams can focus on validation, monitoring, policy governance and post-incident analysis. The benefit is particularly important outside normal working hours, when rapid human escalation may be difficult.
6. Total Cost of Ownership & Energy Planning
A 1U dedicated appliance can simplify rack planning compared with larger mitigation platforms, but full ownership cost includes support, optional reputation services, optics, implementation, spare strategy, power, rack space and staff training. FourTeck recommends comparing a three- or five-year operational view rather than hardware price alone.
Key Hardware & Software Highlights
| Capability | Technical Detail | Operational Outcome |
|---|---|---|
| Inspection | Up to 8 Gbps / 9 Mpps | Capacity for dedicated inline analysis and mitigation. |
| TCP scale | More than 4 million sessions | Supports connection-heavy public services and attack handling. |
| DNS/NTP | More than 2 million responses/s | Dedicated capacity for commonly abused infrastructure protocols. |
| Bypass | Integral bypass on selected RJ45 and LC SR pairs | Supports network continuity planning for inline deployment. |
| Power | Dual redundant AC supplies | Allows A/B feed design where rack power supports it. |
| Storage | 480 GB SSD | Local system and reporting storage capacity. |
The combination of copper, fixed short-reach optical and SFP interfaces makes interface planning unusually important. The four GE RJ45 defence pairs with integral bypass are useful where the inline handoff is copper. Two GE LC SR multimode 850 nm pairs provide optical connectivity with integral optical bypass. Two GE SFP pairs add transceiver flexibility but are specified without bypass protection. Network engineers should map each proposed protected link to the correct pair type before ordering. A diagram showing upstream router, FortiDDoS pair, downstream firewall or switch, management network and HA peer can prevent expensive cabling changes during installation.
Technical Specifications Ledger
| Specification | FortiDDoS 200F | Procurement Note |
|---|---|---|
| Order SKU | FDD-200F | Use manufacturer order code when validating BOM. |
| Inspected mitigation | 8 Gbps / 9 Mpps | Size against both bandwidth and packet rate. |
| TCP sessions | >4 million | Review concurrent connection profile. |
| DNS/NTP mitigation | >2 million responses/s | Relevant for DNS/NTP-heavy environments. |
| Time to mitigation | <1 second | Designed for rapid autonomous response. |
| RJ45 defence pairs | 4 pairs GE RJ45 with integral bypass | Confirm copper handoff and patching. |
| Fixed optical defence pairs | 2 pairs GE LC SR MM 850 nm with integral optical bypass | Confirm multimode fiber and distance. |
| SFP defence pairs | 2 pairs GE SFP, no bypass | Specify compatible transceivers separately where needed. |
| Management | 2 x GE RJ45 | Plan secure management VLAN/IP addressing. |
| Storage | 480 GB SSD | Define external retention requirements separately. |
| Power | Dual redundant AC | Prefer independent A/B rack feeds. |
| Form factor | 1U | Reserve rack depth and service clearance after validating current hardware guide. |
| Modern protocol mitigation | Advanced DNS/NTP, DTLS, QUIC | Map protection requirements to public application protocols. |
Specifications should be treated as engineering limits and purchasing references, not as a substitute for workload analysis. Published maximums are useful for comparing models, but production traffic contains variable packet sizes, protocol distributions and bursts. The safest procurement method is to capture representative peak utilization and packet-rate telemetry, identify the largest plausible legitimate event, estimate attack exposure and then retain operational headroom. Exact chassis dimensions, maximum power consumption, heat output, environmental limits and regulatory compliance should be validated against the current manufacturer hardware documentation at quotation stage because those values can be revision-sensitive and should not be guessed in a purchase specification.
Configuration & Sizing Worksheet
Step 1 — Establish Workload and Scale
Record Internet circuit capacity, 95th-percentile utilization, observed peak Gbps, peak Mpps, concurrent TCP sessions, DNS response rates, public prefixes and critical services. Do not size solely from contracted bandwidth. Packet rate can become the limiting factor during small-packet attacks. Add expected growth for the intended hardware lifecycle. If a planned upgrade could push inspected traffic close to 8 Gbps or packet rate near 9 Mpps, compare a larger model before committing.
Step 2 — Map the Physical Path
Draw each protected link from upstream router or provider handoff through the FortiDDoS defence pair to the downstream firewall, switch or load balancer. Identify copper versus multimode optical connectivity and whether bypass is required. The 200F has multiple pair types with different bypass characteristics, so this mapping determines which interfaces can be used. Verify fiber wavelength, connector type, patch lead length and any SFP requirements.
Step 3 — Validate Rack, Power and Environment
Reserve 1U rack space plus suitable front and rear service clearance. Confirm rack depth, rail compatibility, airflow direction and cable management. Dual redundant AC supplies deliver the greatest resilience when connected to independent protected power feeds. Where both supplies connect to one PDU or one UPS, power-supply redundancy does not protect against failure of that upstream power source. Validate maximum power and heat figures from current manufacturer documentation when planning UPS and cooling capacity.
Step 4 — Select Services and Support
The base appliance provides autonomous mitigation functionality without requiring a mitigation subscription for the core capability, while optional FortiGuard IP Reputation and Domain Reputation services and Fortinet support contracts can be selected according to operational requirements. Current ordering guidance lists dedicated service SKUs for the 200F. Organizations with strict availability targets should align support response expectations, spare strategy and internal escalation procedures with the business impact of downtime.
Step 5 — Prepare the Quote Package
A useful quotation request should include quantity, deployment site, required delivery date, Internet bandwidth, peak traffic, interface media, HA requirement, support duration, optional reputation services, optics, installation or staging needs and any procurement documentation requirements. Government and regulated buyers may also need manufacturer authorization, compliance documents, serial-number records, tax documentation or formal warranty statements. Supplying these requirements early reduces quotation revisions.
Deployment Scenarios & Industry Use Cases
Large Enterprise and Multi-Site Networks
A large enterprise may centralize public applications, VPN services, DNS, remote-access gateways and partner connections in a primary data centre. In this topology, the 200F can be placed inline near the Internet edge, ahead of downstream security and application infrastructure. The key design question is whether all protected traffic traverses the appliance and remains within its capacity envelope. Multi-site businesses should also consider whether protection is needed at each independently connected site or only at centralized Internet exits.
Financial and Banking Institutions
Banks and financial organizations have low tolerance for interruption to online banking, payment interfaces, partner APIs and customer portals. DDoS protection should therefore be integrated into a broader continuity architecture that includes redundant carriers, resilient DNS, application security, firewalls, monitoring and incident response. The 200F can provide dedicated inline mitigation for an appropriately sized edge. Procurement should include documented failover tests, management access controls, logging requirements and support escalation procedures.
Educational and Campus Networks
Universities and large educational institutions often operate diverse Internet services: student portals, learning platforms, research systems, DNS, email gateways and public websites. Traffic can vary sharply around registration, examinations and major events. This variability makes baselining important. A protection platform should distinguish legitimate seasonal surges from hostile traffic while giving network teams visibility into anomalies. Capacity planning should also consider high-volume research traffic and future bandwidth upgrades.
Government and Public-Sector Procurement
Government networks may protect citizen services, ministry portals, public information systems and inter-agency applications. Procurement frequently requires a more formal technical schedule, warranty statement, support scope, delivery documentation and acceptance procedure. FourTeck can structure the quotation around a defined bill of materials and assist with staging requirements. Sensitive deployments should keep detailed topology and addressing information within approved technical channels rather than general commercial correspondence.
Technical Deep Dive: Processing, Acceleration & Traffic Handling
The essential engineering requirement for DDoS mitigation is deterministic traffic handling under stress. Attackers deliberately attempt to create conditions that exhaust bandwidth, packet-processing capacity, connection tables or application resources. FortiDDoS approaches the problem as a dedicated inline system rather than asking a general-purpose perimeter device to absorb every attack function. The 200F’s 8 Gbps and 9 Mpps inspected limits illustrate why both byte rate and packet rate must be modeled. At smaller packet sizes, packets-per-second demand rises rapidly even when aggregate bandwidth is unchanged.
Full packet inspection is significant because sampled monitoring can miss short-lived or distributed anomalies. Fortinet describes FortiDDoS as inspecting traffic rather than relying on sampling, with mitigation designed to occur in less than one second. For operations teams, the practical benefit is fast local enforcement at the protected edge. It also means the appliance must be sized with enough headroom to inspect legitimate peak traffic while attack conditions are present.
The system’s support for millions of TCP sessions and high DNS/NTP response rates addresses distinct resource-exhaustion patterns. Connection-oriented attacks may attempt to consume state, while reflection and amplification techniques can create very high volumes of UDP traffic. Modern DTLS and QUIC support broadens coverage to newer application transports. Buyers should inventory protocols used by critical applications and include them in acceptance testing.
Technical Deep Dive: Software Ecosystem, Firmware Security & Operational Control
A DDoS appliance is not a set-and-forget purchase. The operating model should include firmware governance, configuration backup, administrator access control, monitoring, alert review, incident reporting and periodic validation of thresholds and baselines. Change control is especially important for an inline device because configuration errors can affect production traffic. Organizations should define maintenance windows, rollback plans and configuration ownership before deployment.
FortiGuard IP Reputation and Domain Reputation services are available as separate orderable services for the 200F. These services can add current reputation context to operational decisions, while the core FortiDDoS mitigation capability remains purpose-built for autonomous protection. Buyers should distinguish optional service subscriptions from hardware support. Support contracts address vendor assistance and lifecycle support, while reputation services provide specific intelligence feeds. They are different budget lines and should be itemized clearly in the quote.
Firmware should be managed under the organization’s security maintenance policy. Before production rollout, teams should document the approved release, review relevant release notes, back up configuration and test critical traffic paths. Where a pair of appliances is deployed for high availability, upgrade sequencing should be designed to preserve service continuity. FourTeck can assist with pre-shipment firmware alignment and staging when agreed in the project scope.
Technical Deep Dive: High Availability, Redundancy & Disaster Recovery
Availability design begins by identifying failure domains. Dual power supplies protect against a single PSU failure only when the surrounding power architecture is also redundant. Bypass interfaces can support continuity for an inline path, but bypass behavior must be tested in the actual topology. High availability between appliances can address additional failure scenarios, but it requires suitable network design, cabling, management and operational procedures.
A disaster-recovery plan should document what happens if the appliance, a link, a switch, an upstream router, a power feed or the entire site fails. DDoS protection is one layer within that plan. For organizations with secondary data centres, determine whether the DR site has independent mitigation capacity and whether DNS or routing failover could move traffic to an unprotected path. A failover plan that restores application reachability but removes DDoS protection can introduce a new vulnerability during an incident.
Acceptance testing should include normal traffic, controlled failover, management-plane access, power-supply loss, approved bypass behavior and monitoring alerts. The purpose is not to simulate uncontrolled hostile traffic but to verify that the designed resilience mechanisms behave as documented. Results should be retained with the network runbook so operators know the expected state during an actual fault.
Pre-Purchase Buyer Gap Checklist
Are there hidden recurring costs? Core autonomous mitigation is positioned without an additional mitigation subscription, but buyers may choose separate FortiGuard IP Reputation or Domain Reputation services and should normally budget for an appropriate Fortinet support contract. Ask for every recurring line item to be shown separately with term length and renewal basis.
Will the appliance fit the planned network links? The 200F is a Gigabit-interface platform with a specific combination of RJ45, fixed LC SR multimode and SFP defence pairs. Do not assume any port can be substituted for any other. Match the proposed inline path to the actual interface type and bypass requirement.
Is 8 Gbps enough? It may be more than enough for one environment and insufficient for another. Compare normal peak inspected traffic and packet rate against the platform limits, then include growth and attack headroom. If a near-term circuit upgrade will exceed the comfortable operating range, evaluate larger FortiDDoS models before purchase.
What about rack depth, heat and power? The appliance is 1U, but height alone is not enough for cabinet planning. Validate chassis depth, rail clearance, cable bend radius, maximum power and thermal output from current manufacturer hardware documentation. Confirm two suitable AC feeds if redundant power is part of the design.
Does it replace the firewall? No. A dedicated DDoS appliance protects service availability against denial-of-service behavior; it should operate as part of a layered architecture that can include firewalls, application controls, endpoint protection, identity systems, secure DNS and monitoring.
What should be tested before go-live? Validate interface mapping, management addressing, routing transparency, baseline learning, policy behavior, logging, alert delivery, bypass or HA behavior, configuration backup and rollback. Record the results in the implementation runbook.
How should lifecycle risk be handled? Confirm current manufacturer sale status, support term availability and expected lifecycle at quotation time. Avoid designing a multi-year project around assumptions copied from an old proposal. Hardware availability, service SKUs and firmware recommendations can change.
Uganda Regional Procurement & Delivery Logistics
FourTeck Uganda can structure a FortiDDoS 200F quotation around the required appliance quantity, support term, optional reputation services, accessories and deployment assistance. Enterprise buyers should provide the delivery location, desired schedule and any mandatory procurement documentation at the beginning of the request. This is particularly useful for formal tenders, project-based purchasing and regulated organizations where the commercial response may need to match a technical schedule exactly.
Lead time should be confirmed at quotation because enterprise security appliances can be subject to distributor stock, manufacturer allocation, international freight and import processing. A project plan should not assume immediate availability until the specific bill of materials has been checked through the supply chain. Where the deployment date is fixed, allow time for receiving inspection, staging, firmware alignment, configuration preparation, rack installation and acceptance testing.
Pre-configuration can be scoped where the customer supplies an approved implementation template. This may include management addressing, administrative settings, interface preparation, baseline configuration and firmware alignment. Production routing, addressing and security-sensitive information should be exchanged through appropriate controlled channels. The final configuration remains subject to customer review and site-specific validation.
Local Coverage Matrix
Kampala
Primary enterprise, data-centre, financial and public-sector procurement coordination.
Entebbe
Support for commercial, institutional and connectivity projects requiring enterprise edge protection.
Jinja
Supply coordination for industrial, educational and multi-site business environments.
Mbarara
Regional enterprise and institutional project quotation and delivery planning.
Gulu
Procurement support for organizations extending resilient digital services into northern Uganda.
Coverage planning should distinguish commercial delivery from on-site engineering. If installation, rack work, migration assistance or acceptance testing is required outside the primary service area, include that requirement in the quotation request so travel, scheduling and technical scope can be defined before purchase.
Cross-Border & Regional Supply Chains
Organizations operating across East Africa, the Gulf and wider African markets may need consistent product selection and support planning across multiple countries. FourTeck regional sites can help coordinate requirements through Uganda, Kenya, Africa, UAE and Kuwait. Cross-border projects should keep model, support term and interface requirements consistent while accounting for local import, delivery, tax and installation conditions.
For multi-country rollouts, create a master bill of materials and then a country-specific schedule showing quantity, ship-to site, local power requirements, support entitlement, optics and target installation date. This reduces model drift and helps operations teams standardize documentation and spares.
Related Products & Infrastructure Planning
A complete edge-protection project may require more than the FortiDDoS appliance itself. Buyers can review the FourTeck Uganda enterprise technology portfolio for complementary network security, switching, routing, rack, power and connectivity requirements. Where inspected traffic exceeds the 200F design range, ask for comparison with larger FortiDDoS models such as the 1500F or 2000F. Where virtualization is preferred, FortiDDoS virtual appliance options may also be considered after validating hypervisor and performance requirements.
Related bill-of-material items can include compatible optical transceivers, multimode fiber patch leads, copper patching, rack PDUs, UPS capacity, management switches and console access. The correct accessory set depends on the physical topology. FourTeck recommends ordering critical connectivity items with the appliance rather than discovering interface gaps during installation.
FourTeck Technical Service Capabilities
FourTeck can support engineering validation before order placement by reviewing the proposed model, interface requirements, traffic capacity, redundancy assumptions and support selections. Bill-of-material verification helps ensure the manufacturer appliance code, service SKUs and required accessories are aligned with the intended deployment. This is especially useful when a customer has inherited an older specification or when the project has evolved since the original design.
Staging services can be defined for projects that need equipment prepared before shipment. Depending on agreed scope, this can include physical inspection, serial-number capture, firmware alignment, management configuration, configuration template loading and basic readiness checks. Pre-shipment firmware work should follow an approved target release rather than simply installing the newest available version without change control.
Post-sales technical support can assist with deployment coordination, configuration questions, troubleshooting preparation and vendor escalation under the applicable support entitlement. Customers should define who owns production changes and who has authority to approve mitigation policy changes. Clear responsibility reduces delay during incidents and keeps the operational process auditable.
Extended Technical FAQ
1. What capacity does FortiDDoS 200F provide?
FortiDDoS 200F is specified for up to 8 Gbps inspected mitigation and 9 million packets per second. It also supports more than four million TCP sessions and more than two million DNS/NTP responses per second, with a stated mitigation time below one second. These figures should be evaluated together. A small-packet flood can create a high packet rate without using the full nominal bandwidth, so procurement teams should collect both Gbps and Mpps telemetry. Leave headroom for legitimate bursts, attack conditions and future circuit growth rather than designing exactly to a published maximum.
2. Does FortiDDoS 200F require a recurring mitigation subscription?
Fortinet positions FortiDDoS autonomous mitigation without requiring an additional subscription for the core mitigation function. However, optional FortiGuard IP Reputation and Domain Reputation services are separately orderable, and organizations should also select an appropriate Fortinet support contract for vendor assistance and lifecycle coverage. Ask for these components to be itemized separately in the commercial quotation. This makes first-year and renewal costs easier to understand and prevents optional intelligence services from being confused with the hardware’s base mitigation capability.
3. Can FortiDDoS 200F be installed on an optical Internet link?
Yes, but the exact optical handoff matters. The appliance includes two pairs of Gigabit Ethernet LC short-reach multimode 850 nm interfaces with integral optical bypass, plus two pairs of Gigabit Ethernet SFP interfaces without bypass protection. Confirm fiber type, wavelength, connector, link distance and transceiver requirements before ordering. If the provider handoff or internal network uses a different speed or optical standard, the 200F may not be the correct physical fit. A simple link diagram reviewed before purchase can prevent a major installation delay.
4. How does bypass affect network continuity?
Bypass is designed to help preserve the physical traffic path under defined appliance conditions when using supported bypass-capable defence pairs. The 200F includes integral bypass on four GE RJ45 pairs and two GE LC SR multimode optical pairs. Its two GE SFP pairs are specified without bypass protection. Bypass should not be treated as a complete high-availability design by itself. Network architects should document expected behavior during appliance failure, power loss, maintenance and HA failover, then test those scenarios during commissioning.
5. Is the 200F suitable for banks and regulated organizations?
It can be suitable where the traffic profile and interface requirements fit the platform capacity. Financial organizations should treat the appliance as one component of a layered availability architecture. The project should include redundant connectivity, secure management, logging, configuration backup, change control, incident procedures and an appropriate support plan. Regulatory and audit requirements differ by organization, so retention, access control and evidence requirements should be documented before implementation. FourTeck can assist with the hardware and service bill of materials while the customer’s governance team defines policy obligations.
6. What information is needed for accurate sizing?
Provide contracted Internet capacity, observed peak Gbps, peak packets per second, concurrent TCP sessions, DNS/NTP traffic where relevant, public address ranges, application protocols, number of protected links, interface media, expected annual growth and resilience requirements. Also mention any planned bandwidth upgrade during the intended hardware lifecycle. If telemetry is unavailable, collect representative data before finalizing the model. Buying solely from current circuit speed can overlook packet-rate exposure and future growth, while buying solely from attack headlines can lead to unnecessary over-sizing.
7. What support options should be considered?
Current FortiDDoS ordering guidance provides dedicated 24×7 support options for the 200F in multi-year terms, along with separate IP Reputation and Domain Reputation service codes. The right support term depends on business criticality, internal engineering capability, procurement cycle and replacement strategy. Organizations that cannot tolerate extended downtime should align vendor support with a documented spare and escalation plan. Confirm exact service SKUs, entitlement scope and term at quotation because ordering guides can change over the product lifecycle.
8. Can FourTeck pre-configure the appliance before delivery?
Pre-configuration can be scoped where the customer provides an approved design and required configuration inputs. Typical staging can include firmware alignment, management settings, interface preparation, configuration template loading and basic validation. Sensitive production details should be shared through approved channels. The customer should retain final change authority and perform site acceptance testing because live routing, carrier handoffs, cabling and surrounding infrastructure cannot be fully validated away from the production environment.
9. Does FortiDDoS replace upstream carrier mitigation?
Not necessarily. An on-premises appliance protects traffic that can physically reach the customer edge. If an attack exceeds the capacity of the Internet circuit itself, upstream carrier or cloud-based scrubbing may still be required because a saturated access link cannot be repaired solely by an appliance behind that link. Many organizations therefore use layered protection: upstream capacity or scrubbing for very large volumetric events and an inline appliance for local, granular and autonomous mitigation. The appropriate architecture depends on circuit size, threat exposure and availability objectives.
10. What should be included in the purchase order?
The purchase package should identify the FDD-200F appliance quantity, selected support term, any IP or Domain Reputation services, required optics and cabling, delivery site, installation or staging scope and any documentation requirements. If high availability requires two appliances, state that explicitly. For formal procurement, also specify required warranty documentation, manufacturer authorization where applicable, tax documents, delivery acceptance process and target schedule. A complete bill of materials reduces the risk of receiving the appliance without a required service or connectivity component.
Plan Your FortiDDoS 200F Deployment in Uganda
A successful DDoS protection purchase starts with accurate traffic sizing, interface validation and a clear continuity design. Share your Internet capacity, peak packet rate, protected services, link media, redundancy requirement and preferred support term with FourTeck. The resulting quotation can then be structured around the correct appliance, support coverage, optional reputation services, connectivity accessories and implementation scope. For multi-site or cross-border projects, include each location and target deployment date so the bill of materials can remain consistent across the rollout.
FortiDDoS 200F is a strong fit for organizations whose protected traffic sits comfortably within its 8 Gbps and 9 Mpps inspected limits and whose network can use its Gigabit defence interfaces. Where capacity, interface speed or future growth exceeds that profile, FourTeck can help compare larger FortiDDoS models before the order is committed.

Reviews
There are no reviews yet.