
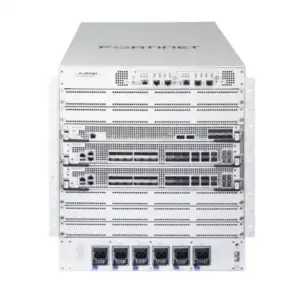
Fortinet FortiPAM 3000G Privileged Access Management Appliance for Uganda
Fortinet FortiPAM 3000G is a dedicated privileged access management and secure remote access appliance built for organizations that must control how administrators, engineers, vendors and service teams reach sensitive infrastructure. The platform places privileged credentials, approval rules, access policies and session evidence under centralized governance instead of leaving powerful passwords scattered across endpoints, spreadsheets, shared vaults or individual administrator knowledge. Fortinet identifies the FPA-3000G as the FortiPAM 3000G hardware appliance for up to 100 users, with stackable hardware user upgrades available when an organization needs additional capacity.
For Ugandan enterprises, this model is particularly relevant where privileged access spans data centers, branch networks, server environments, databases, network devices, cloud-connected resources and operational technology. It supports a structured approach in which users can be granted access according to role, approval workflow and policy without unnecessarily exposing the underlying credential. Session monitoring and recording provide accountability for sensitive administrative activity, while automated password management helps reduce the risk created by static or reused privileged credentials.
Procurement teams should treat FortiPAM as a security platform rather than a simple rack appliance. The final bill of materials can depend on privileged-user count, high-availability requirements, FortiCare support, optional antivirus and data-leak-prevention protection, network topology, authentication design, session retention and deployment scope. FourTeck can help validate these dependencies before purchase so the delivered system matches the intended operating model.
Instant Procurement Facts
FortiPAM 3000G
FPA-3000G
Privileged access management and secure remote access
Up to 100 users
Stackable hardware user upgrades
Quote-based enterprise procurement
The appliance is intended for organizations that want a controlled gateway between privileged users and protected resources. Hardware user upgrades are available in increments including 25, 50, 100 and 200 users. Because licensing and support choices affect the complete order, buyers should provide the expected privileged-user population and whether high availability is required when requesting a quotation. High-availability nodes should be aligned to the same license type. Physical interface, electrical, environmental and dimensional requirements should be checked against the current Fortinet hardware guide and the exact shipping configuration before rack planning.
Operational Architecture and Security Overview
Privileged credentials represent a concentrated security risk because they can unlock servers, databases, network equipment, security consoles and operational systems. FortiPAM changes the access model by allowing credentials to be stored and governed centrally. Authorized users can reach permitted resources through controlled workflows while the platform manages the secret behind the connection. This reduces the need for administrators to know, copy or locally retain sensitive passwords and keys.
Credential lifecycle management is a core architectural function. FortiPAM can discover and onboard unmanaged privileged accounts, store passwords, SSH keys, API tokens and certificates, and apply automated password creation and rotation. This is operationally important when an organization has inherited years of administrator accounts or service credentials with inconsistent ownership. Rather than treating remediation as a one-time password-cleanup exercise, teams can establish ongoing policies for credential handling.
Access governance adds another control layer. Policies can determine which users may access specific secrets or systems, and approval processes can be used where privileged activity requires authorization. Role-based controls, identity-provider integration and adaptive authentication options allow the access path to reflect the sensitivity of the target. FortiPAM also supports protocol-oriented access patterns including RDP, SSH, VNC and web access, enabling security teams to bring multiple administrative workflows into a common governance framework.
Session monitoring is essential where organizations need to establish who accessed a resource, when the access occurred and what happened during the session. FortiPAM can monitor and record privileged sessions, including activity evidence such as keystrokes and mouse events. Command and SSH filtering can further restrict dangerous or unauthorized operations. These controls help incident responders, auditors and system owners move beyond simple login records toward richer evidence of privileged activity.
Secure remote access extends the value of the platform to third-party maintenance and geographically distributed support teams. Instead of opening broad network paths or distributing permanent administrator credentials to external parties, organizations can create narrower, policy-governed access. This is relevant to Ugandan enterprises that rely on international vendors, regional support partners or specialists who must maintain infrastructure without receiving unrestricted network privileges.
The 3000G is also suited to environments with substantial configuration scale. Published Fortinet maximum-value documentation for the platform shows higher object limits than the smaller 1000G in areas such as secret folders, databases, requests, zones and administrator objects. Procurement teams should still size based on current software release limits and actual workflows, because configuration-object maximums are not equivalent to simultaneous session capacity or storage-retention guarantees.
Enterprise Business Outcomes
1. Privileged Access Integrity
Central vaulting and controlled credential delivery reduce dependence on manually shared administrator passwords. Automated rotation can shorten the useful life of exposed credentials and improve consistency across protected systems.
2. Operational Reliability
Defined roles, approval paths and repeatable access policies make privileged operations less dependent on informal processes. High-availability planning can be incorporated where access to critical systems must remain resilient during appliance or maintenance events.
3. Scalable Governance
The FPA-3000G starts with support for up to 100 users and can be expanded using stackable hardware user upgrades. This gives growing organizations a path to extend privileged-user capacity without immediately changing the appliance family.
4. Stronger Access Control
Role-based authorization, secret permissions, approval workflows, authentication integrations and protocol-aware controls help organizations enforce least-privilege principles across administrative and third-party access.
5. Central Operational Visibility
Session monitoring, recording and auditable activity records consolidate evidence that would otherwise be fragmented across target systems. Security and compliance teams gain a clearer view of privileged behavior.
6. Lifecycle Cost Control
A purpose-built appliance can simplify deployment planning for organizations that prefer a dedicated platform. Accurate user sizing, support selection and retention planning help prevent unnecessary license purchases or late project changes.
Key Hardware and Software Highlights
| Capability | Operational Value |
|---|---|
| Dedicated FPA-3000G hardware | Purpose-built deployment option for privileged access governance. |
| Up to 100 base users | Supports enterprise teams with an expandable hardware licensing model. |
| Credential vault | Protects passwords, SSH keys, API tokens and certificates. |
| Automated rotation | Reduces exposure from static privileged credentials. |
| Session recording | Creates evidence for audit, investigation and accountability. |
| Secure remote access | Controls third-party and remote administrative connections. |
| Optional protection services | Antivirus and data-leak-prevention protection can be ordered for the appliance. |
| FortiCare Premium option | Provides vendor support coverage aligned to enterprise operations. |
The strongest benefit comes from combining these capabilities into a controlled privileged-access lifecycle. Discovery identifies accounts that need governance; vaulting protects secrets; approval rules determine when access is allowed; session controls supervise activity; recording creates evidence; and rotation changes credentials after use or according to policy. This sequence can replace fragmented practices with a repeatable security process.
Technical Specifications Ledger
| Item | FortiPAM 3000G |
|---|---|
| Product family | Fortinet FortiPAM |
| Hardware model | FortiPAM 3000G |
| Ordering SKU | FPA-3000G |
| Primary function | Privileged access management and secure remote access |
| Base hardware user limit | Up to 100 users |
| Hardware user upgrades | 25, 50, 100 and 200-user stackable upgrade options |
| Credential types | Passwords, SSH keys, API tokens and certificates |
| Administrative protocols | RDP, SSH, VNC and web-oriented access workflows |
| Session controls | Monitoring, recording, command filtering and SSH filter controls |
| Optional security service | Antivirus and Data Leak Prevention protection |
| Support option | FortiCare Premium Support |
| Secret folder maximum | Published maximum: 6,000 |
| Database maximum | Published maximum: 10,000 |
| Request maximum | Published maximum: 10,000 |
| Zone maximum | Published VDOM limit: 500 |
| Admin maximum | Published global limit: 3,000 |
| Physical dimensions, ports and power | Confirm against current Fortinet 3000G hardware guide and exact order configuration before installation. |
Published configuration maximums are useful for architecture planning but should not be interpreted as guaranteed performance figures. Session concurrency, recording retention, network conditions, software version and workload characteristics can affect practical sizing. For procurement, the safest method is to document expected users, managed secrets, target systems, session types, daily privileged sessions and retention requirements, then validate the proposed design before issuing the purchase order.
Configuration and Sizing Worksheet
1. Estimate privileged workload
Count the people who require privileged access rather than the total employee population. Include infrastructure administrators, database administrators, network engineers, security teams, application support, help-desk escalation staff, contractors and external vendors where accounts will be created for them. The base FPA-3000G supports up to 100 users. If the expected population exceeds that level, identify the required stackable hardware user upgrades during quotation.
2. Inventory protected resources
Build a target inventory covering Windows and Linux servers, databases, network equipment, hypervisors, security appliances, web administration portals and operational technology systems. Record connection protocols and credential types. This reveals where password rotation, SSH key handling, certificates, API tokens or browser-based launchers may be required.
3. Define approval and authentication
Decide which access can be granted directly by role and which must require approval. Identify identity providers, multifactor requirements, device posture controls and whether remote vendors will use agentless or managed endpoint workflows. Approval design should balance security with the response times required by operations teams.
4. Plan rack, power and network connectivity
Reserve appropriate rack space and confirm electrical feeds, network interfaces, cable types, management connectivity and data-center environmental limits using the current hardware documentation. If resilience requires redundant feeds or a second appliance, include those requirements before the rack layout and bill of materials are frozen.
5. Select services and support
Determine whether FortiCare Premium Support and optional Antivirus/Data Leak Prevention protection are required. Support duration should align with internal maintenance policy and project lifecycle. Organizations with strict uptime requirements should also plan high availability and ensure both nodes use compatible licensing.
6. Prepare the quotation brief
Provide the appliance model, user count, upgrade quantity, support term, security services, HA requirement, delivery city, required installation window and any staging expectations. A complete brief reduces back-and-forth and helps ensure that accessories and service entitlements are not missed.
Deployment Scenarios in Uganda
Large Enterprise and Multi-Site Networks
A multi-site enterprise can use FortiPAM 3000G as a centralized privileged-access control point for administrators who manage infrastructure across headquarters, branches, data centers and remote facilities. Instead of maintaining separate privileged credentials for every support team and location, the organization can establish consistent access rules and centralized auditing. This is particularly valuable during staff changes, outsourced support transitions or mergers, when privileged accounts often accumulate without clear ownership.
Financial and Banking Institutions
Banks, payment organizations and financial institutions handle infrastructure where administrator activity must be tightly controlled and traceable. FortiPAM can support segregation of duties by separating credential ownership from credential use, applying approval processes to sensitive systems and recording privileged sessions. The resulting evidence can strengthen internal investigations and compliance processes while password rotation reduces reliance on long-lived shared administrator secrets.
Educational and Campus Networks
Universities and large education environments operate diverse infrastructure with central IT teams, departmental administrators, contractors and equipment vendors. A privileged-access platform can reduce uncontrolled sharing of root, administrator and network-device credentials. Centralized governance is useful where staff turnover, temporary projects and third-party support create frequent changes in who needs elevated access.
Government and Critical Infrastructure
Government departments and critical-service operators can use FortiPAM to create controlled access paths for systems with heightened confidentiality or operational impact. Secure remote access can help govern external maintenance personnel, while recording and approval workflows provide accountability. Procurement teams should align deployment design with applicable internal security policies, records-retention requirements and business-continuity standards.
Technical Deep Dive: Credential and Access Control Engine
FortiPAM is designed around the idea that privileged users should receive authorized access without automatically receiving possession of the privileged secret. The vault stores sensitive credentials and the platform brokers their use. This architecture limits credential exposure on user endpoints and supports automated password changes. Discovery and onboarding capabilities help security teams identify unmanaged accounts and bring them under governance, which is crucial in environments where legacy systems and historical administrator practices have created hidden privileged identities.
Secret permissions, user roles and hierarchical approval workflows allow administrators to map organizational responsibilities into access policy. Rather than assigning broad standing privileges, teams can create narrower access patterns. Protocol-aware controls for RDP, SSH, VNC and web access allow common administrative sessions to be governed through the platform. For organizations implementing zero-trust principles, identity and device posture can become part of the access decision instead of assuming that network location alone establishes trust.
Technical Deep Dive: Software Ecosystem and Operational Control
FortiPAM integrates with broader identity and endpoint controls to support passwordless, single-sign-on and adaptive multifactor workflows where appropriately designed. Fortinet documentation notes that current FortiPAM releases may require specific FortiClient versions for the complete feature set, so upgrade planning should include client compatibility validation. This is important for organizations that manage endpoint software through controlled release rings or have older operating systems that cannot immediately adopt a required client version.
Operational control also includes session supervision. Administrators can monitor active sessions and use command or SSH filtering to limit risky operations. Recording creates a reviewable history that can support investigations and audit requirements. The value is not merely the existence of logs; it is the ability to combine identity, target resource, access approval and session evidence into a coherent privileged-access record.
Technical Deep Dive: High Availability and Recovery Planning
Privileged-access infrastructure can become operationally critical because administrators may depend on it to reach the systems they are responsible for restoring. High-availability planning should therefore be considered early. Fortinet ordering guidance states that nodes in an HA configuration must use the same license type. Procurement teams should account for the second appliance, equivalent licensing and support, network paths and power feeds as part of the initial design rather than treating resilience as an afterthought.
Disaster-recovery planning should document how privileged access will operate during appliance, site, identity-provider or network failures. Organizations should define break-glass procedures that preserve accountability while allowing emergency access. Configuration backup, recovery testing, certificate management, time synchronization and retention of session evidence should be incorporated into operational runbooks. A well-designed PAM deployment must protect credentials without becoming a single unmanaged dependency during an incident.
Pre-Purchase Buyer Gap Checklist
Are there licensing costs beyond the appliance? The base FPA-3000G is specified for up to 100 users. Additional hardware user capacity can be purchased through stackable upgrades. FortiCare Premium Support and Antivirus/Data Leak Prevention protection are separate ordering considerations. Confirm the exact term and quantity on the quotation.
Can capacity grow? Yes. Published hardware upgrades add 25, 50, 100 or 200 users and are stackable. Forecast growth so the initial deployment and authentication design can accommodate future administrators and vendors.
Does HA change the order? Yes. A resilient design normally requires additional hardware and aligned licensing. Fortinet guidance indicates HA nodes must use the same license type, so the architecture should be validated before purchasing.
How much session storage is needed? Recording requirements vary substantially by session duration, protocol, number of users and retention policy. Define retention targets and compliance expectations before sizing. Do not assume that user capacity alone determines recording requirements.
Will it work with existing identity controls? FortiPAM supports identity-provider and authentication integrations, but exact interoperability should be checked against the current software release and your existing directory, MFA and endpoint architecture.
What about rack clearance and power? Confirm the current Fortinet hardware guide for exact physical and electrical specifications before installation. This prevents late changes to PDUs, cabling, rack rails or data-center allocation.
Does every remote user need permanent network access? The platform is intended to provide controlled secure remote access, allowing organizations to reduce broad standing connectivity. The appropriate workflow depends on target protocol, endpoint posture and policy.
What software version should be deployed? Use a release approved for your environment and validate FortiClient compatibility where client-assisted features are required. Firmware and client versions should be included in staging and change-control planning.
Uganda Procurement and Delivery Logistics
FourTeck supports quotation-led procurement for FortiPAM 3000G projects in Uganda. A useful quotation request includes the required number of privileged users, expected growth, support term, optional protection services, HA requirements, delivery destination and any pre-configuration needs. Enterprise orders may require confirmation of lead time and entitlement availability before a delivery commitment is issued.
For projects in Kampala and surrounding commercial areas, procurement teams can coordinate delivery with data-center or office installation schedules. Entebbe deployments can be planned around airport-area businesses, hospitality, logistics and government environments. Jinja, Mbarara and Gulu projects can be supplied with logistics planning appropriate to regional delivery and site readiness. Nationwide projects should identify all destination sites at quotation stage where split shipments or staged rollouts are expected.
Pre-configuration can include agreed baseline tasks such as firmware validation, management addressing, naming conventions or other staging activities when defined in the project scope. Sensitive production credentials should normally be created or imported under the customer’s controlled process. Final delivery timing depends on stock position, import and logistics conditions, order approval and the exact configuration requested.
Local Coverage Matrix
Kampala
Enterprise headquarters, data centers, financial services, telecom and government deployments.
Entebbe
Airport-area operations, logistics, hospitality, public-sector and distributed infrastructure.
Jinja
Industrial, manufacturing, education and regional business infrastructure.
Mbarara
Regional enterprise, healthcare, education and multi-site administration.
Gulu
Institutional, NGO, education and northern-region technology deployments.
Site location affects more than freight. Rack readiness, local engineering access, change windows and the availability of remote stakeholders should be considered when scheduling commissioning. Multi-site customers can standardize the privileged-access policy centrally while planning site-specific target onboarding in phases.
Cross-Border and Regional Supply
Organizations operating across East Africa, the Gulf and wider African markets can coordinate related technology procurement through FourTeck regional channels. Visit FourTeck Uganda for Uganda projects, FourTeck Kenya for Kenyan requirements, FourTeck Africa for broader African supply, FourTeck UAE for United Arab Emirates procurement and FourTeck Kuwait for Kuwait projects.
Regional organizations should standardize the appliance model, license approach, support term and software baseline where possible. Consistent bills of materials simplify spares, engineering procedures and support escalation. Customs, import requirements, delivery lead times and local tax treatment can differ by destination, so cross-border orders should be quoted according to the receiving country rather than assuming one commercial structure applies everywhere.
Related Fortinet Procurement Options
A FortiPAM project commonly intersects with identity, endpoint, firewall and management infrastructure. Buyers can explore the Fortinet product range in Uganda, review enterprise technology solutions, or contact FourTeck for compatible FortiGate, FortiClient and authentication components. Where user growth is expected, request the appropriate FortiPAM hardware user-upgrade SKU together with the appliance. Where operational resilience is mandatory, request a matched second FortiPAM appliance and corresponding support services for HA design.
Accessory planning should cover rack mounting, supported transceivers or network cabling where applicable, power distribution compatibility, console access and any infrastructure required for management or backup connectivity. Exact accessory compatibility should be validated against the current hardware documentation and the specific deployment architecture rather than selected only by connector appearance.
FourTeck Technical Service Capabilities
FourTeck can assist enterprise buyers with pre-order engineering validation and bill-of-materials review. The goal is to identify gaps before shipment: insufficient user licensing, missing support, incomplete HA quantities, incompatible assumptions about identity integration, or overlooked rack and power dependencies. For complex environments, a requirements worksheet can be used to map privileged user groups, protected resources, protocols, approval workflows and retention expectations.
Staging services can be scoped for baseline preparation before shipment. This may include validating the agreed software release, applying approved updates, confirming appliance health and preparing documented configuration elements that do not require exposure of customer production secrets. Customers should maintain controlled procedures for production credentials, certificates and final trust relationships.
Post-sales assistance can support deployment coordination, configuration guidance, troubleshooting and escalation preparation. Where vendor support is included, accurate serial numbers, entitlement records, software versions, diagnostic information and issue timelines help speed case handling. The service scope should be agreed in the quotation so procurement, security and infrastructure teams share the same expectations.
FortiPAM 3000G Technical FAQ
How many users does FortiPAM 3000G support?
Fortinet lists the FPA-3000G hardware appliance for up to 100 users in its base configuration. If an organization needs more capacity, stackable hardware user upgrades are available in 25, 50, 100 and 200-user increments. User count should be calculated around the people who need accounts in the privileged-access platform, including administrators and applicable third parties. Forecast expected growth over the planned appliance lifecycle so the initial architecture is not sized only for today’s team.
What does FortiPAM protect?
FortiPAM protects privileged accounts, credentials and administrative access paths. It can securely store passwords, SSH keys, API tokens and certificates, apply permissions and approval workflows, rotate credentials and broker sessions to target resources. It is relevant to servers, network devices, databases, applications, security infrastructure and operational technology where elevated access must be governed. Exact target compatibility and launcher behavior should be validated for the software release and systems in your environment.
Can FortiPAM 3000G record administrator sessions?
Yes. FortiPAM provides privileged session monitoring and recording, including activity evidence such as logins, keystrokes and mouse events. Administrators can also use command filtering and SSH filter controls to restrict certain actions. Recording requirements should be planned alongside retention policy because session volume and duration influence storage consumption. Organizations should define who may review recordings, how long evidence must be retained and how access to sensitive recordings will itself be controlled.
Does FortiPAM eliminate the need to share administrator passwords?
It is designed to greatly reduce direct credential exposure by storing privileged secrets in a controlled vault and delivering access through governed sessions. Users can access authorized resources without necessarily knowing the underlying credential. Automated password rotation further reduces the usefulness of credentials that may have been exposed previously. Some emergency or legacy workflows may still require carefully controlled exceptions, so organizations should define break-glass procedures and migrate unmanaged access patterns in stages.
Is FortiCare included with FortiPAM 3000G?
Fortinet publishes FortiCare Premium Support as a separate ordering line associated with the FPA-3000G. The exact support term and entitlement should therefore be explicitly shown on the supplier quotation. Support planning matters for enterprise deployments because access to vendor assistance, updates and replacement processes can affect operational continuity. Buyers should align the support period with the organization’s maintenance lifecycle and renewal calendar rather than assuming the hardware purchase alone defines long-term coverage.
Are antivirus and data-leak-prevention services available?
Yes. Fortinet lists an Antivirus and Data Leak Prevention protection option for the FortiPAM 3000G. This can add controls around malware and data misuse or exfiltration risks in supported workflows. Whether it is required depends on the organization’s security architecture and the role FortiPAM will play in remote and privileged sessions. Ask for the relevant service SKU and term to be identified separately on the quotation so there is no ambiguity about what protection is included.
Can FortiPAM 3000G be deployed in high availability?
Fortinet provides guidance for HA deployments and notes that each HA node must use the same license type. A resilient design should therefore be treated as a multi-appliance project with matching licensing, support, network connectivity and power planning. The customer should also document failure scenarios and recovery procedures. High availability reduces appliance-level disruption risk, but complete privileged-access continuity also depends on identity services, network paths, DNS, time services and the availability of protected target systems.
Does FortiPAM support remote vendors and contractors?
Secure remote and third-party access is a major FortiPAM use case. Organizations can create policies that give vendors access only to approved resources and revoke that access when it is no longer required. Sessions can be monitored and recorded, helping reduce the risk associated with permanent VPN access or shared credentials. The final design should define vendor identity verification, endpoint requirements, approval workflow, allowed protocols, permitted maintenance windows and how emergency access requests are handled.
What should be checked before ordering the appliance?
Confirm privileged-user count, expected growth, protected target systems, protocols, authentication design, approval workflows, session-recording requirements, retention policy, HA needs, support term and optional security services. Separately validate physical rack dimensions, power feeds, interfaces and cabling against the current Fortinet hardware documentation. If client-assisted features are planned, verify FortiClient version compatibility with the intended FortiPAM release. Providing this information at quotation stage helps avoid incomplete bills of materials and delayed deployment.
Can FourTeck assist with configuration and delivery in Uganda?
FourTeck can support quotation preparation, bill-of-materials validation, regional delivery planning and agreed staging or configuration assistance for Uganda deployments. Projects can be coordinated for Kampala, Entebbe, Jinja, Mbarara, Gulu and other locations. The appropriate service scope depends on whether the customer needs supply only, pre-shipment staging, deployment guidance or broader implementation assistance. Provide the project location, user count, target timeline and technical requirements when requesting a quotation so the commercial and engineering scope can be aligned.
Request a Fortinet FortiPAM 3000G Quote for Uganda
For an accurate FortiPAM 3000G proposal, send your expected privileged-user count, deployment city, support duration, HA requirement, optional protection requirements and planned installation timeline. FourTeck can review the bill of materials and help align appliance capacity, user upgrades and support services with the intended privileged-access architecture. Organizations with multi-site or regional deployments can also request coordinated supply planning across supported FourTeck markets.

Reviews
There are no reviews yet.