FortiGate 900G in Uganda
A 1RU next-generation firewall for high-capacity enterprise edge security, secure SD-WAN, segmentation, VPN and application-aware threat inspection.
Fortinet positions the 900G series for organisations that need accelerated security processing, deep traffic visibility and flexible high-speed interfaces. FourTeck can help size the appliance against real WAN throughput, inspection policy, VPN demand, availability architecture and subscription requirements before a Uganda quotation is prepared.
Fortinet
FG-900G
Enterprise NGFW
1RU rack mount
FortiOS / Fortinet ecosystem
Configuration dependent
A high-capacity security platform for demanding network edges
The FortiGate 900G is designed for organisations whose firewall is no longer a simple internet gateway. In a large campus, data centre, multi-site headquarters environment or high-volume enterprise edge, the security appliance may be expected to inspect encrypted sessions, enforce application policy, terminate virtual private networks, segment internal zones, route traffic between services and participate in a broader secure networking architecture. That combination makes sizing more important than simply matching the nominal speed of an internet circuit.
Fortinet’s current product information describes the 900G series as an AI and machine-learning enabled next-generation firewall with Fortinet ASIC acceleration. The platform uses FortiOS to combine networking and security functions, while FortiGuard services add subscription-based threat intelligence and security controls. Universal zero-trust network access, secure SD-WAN, segmentation and SSL inspection are among the functions that make the appliance relevant where organisations want policy enforcement to follow users, applications and traffic patterns rather than rely only on ports and IP addresses.
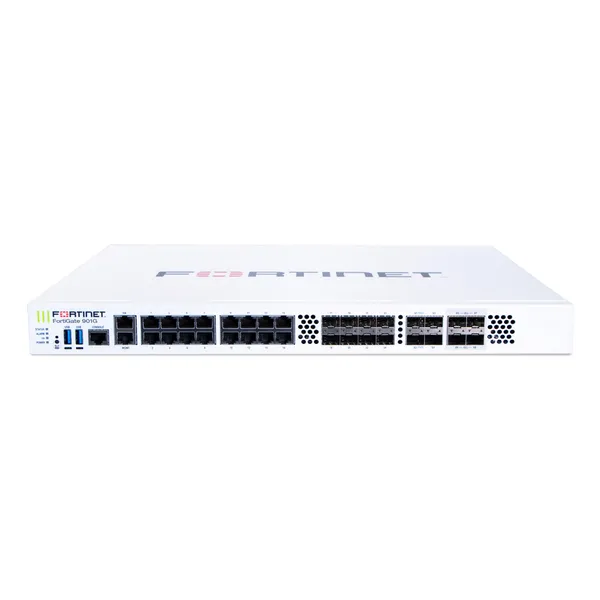
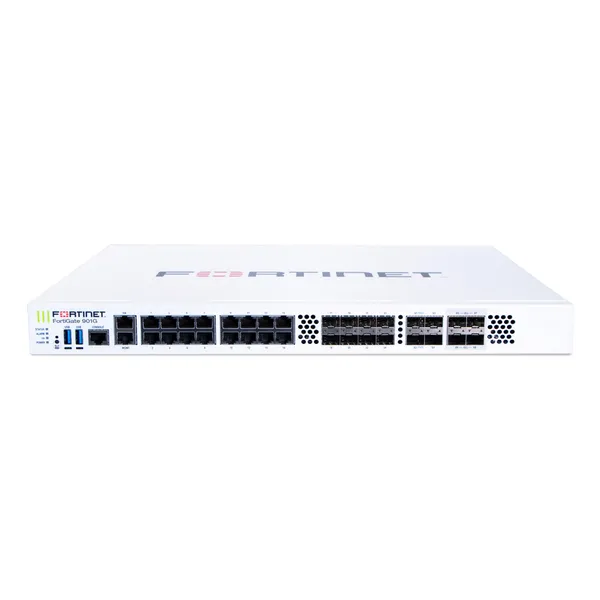
Hardware flexibility is another important part of the model. The FG-900G includes sixteen Gigabit Ethernet RJ45 data ports, eight Gigabit Ethernet SFP slots, four 10GE/GE SFP+/SFP slots and four 25GE/10GE SFP28/SFP+ ultra-low-latency slots, plus dedicated management and HA connectivity. This mix allows designers to combine copper access, fibre handoffs and higher-speed uplinks without forcing every connection into the same media type. Transceivers, direct-attach cables and fibre patching should still be confirmed against the actual switch, carrier and data-centre design.
For Uganda buyers, the most important purchasing task is to define what the firewall must inspect and for how long the supporting security services are required. The base appliance and a bundle that includes FortiCare plus FortiGuard services are different procurement choices. High-availability projects also need two correctly matched appliances and a clear plan for interfaces, power, cabling, routing and failover testing. FourTeck can help convert these requirements into a practical bill of materials and quote.
Why the 900G can simplify a high-throughput security edge
01
Accelerated security processing
Fortinet’s NP7 and CP9 security processors are used to offload appropriate network and content-security functions. The practical value is greater room to apply security services without relying only on general-purpose CPU processing, which matters when many concurrent flows are active.
02
High-speed interface flexibility
The combination of 25GE, 10GE, GE fibre and copper ports lets network architects map carrier links, core-switch connections, server zones and management functions to appropriate media. This reduces the chance that a capable firewall becomes constrained by an inflexible physical interface plan.
03
Converged security and SD-WAN policy
FortiOS combines firewalling with secure SD-WAN capabilities, so path selection and security controls can operate in the same platform. For multi-site organisations this can reduce the operational split between a WAN edge device and a separate security gateway.
04
Segmentation for risk containment
A large firewall can enforce policy between user networks, servers, internet-facing services, branch tunnels and other trust zones. Correctly designed segmentation limits unnecessary lateral reach and gives administrators more precise control over which applications and systems may communicate.
05
Centralised operational options
The wider Fortinet ecosystem supports centralised management and analytics options for organisations with multiple FortiGate appliances. This becomes useful when policy consistency, change control and reporting must scale beyond one device.
06
A platform with room for growth
Substantial session, VPN and inspection capability can give an enterprise more headroom than branch appliances, but that headroom should be validated against real policy. Capacity planning should include encrypted traffic growth, additional sites, cloud connections and future threat-protection profiles.
Built around fast inspection, deep visibility and a broad interface mix
The distinction of the 900G is not a single headline feature. It is the combination of high-throughput hardware acceleration, FortiOS security and networking functions, FortiGuard subscription services, and physical interfaces that can connect to modern enterprise cores. That combination is useful when the firewall is expected to be a security enforcement point as well as a routing, VPN and WAN edge.
Vendor-rated baseline firewall performance under the stated test conditions.
Useful for high-bandwidth core, aggregation and data-centre connectivity.
Firewall, SD-WAN, ZTNA and segmentation functions operate in one platform.
Supports resilient appliance power design; exact AC or DC model must be selected.
FortiGate 900G technical details
| Specification | FG-900G |
|---|---|
| Product type | Next-generation firewall / secure networking appliance |
| Firewall throughput | Up to 164 Gbps, based on vendor test methodology |
| IPS throughput | Vendor-rated performance varies by current datasheet revision and test profile; confirm against the latest Fortinet 900G data sheet for procurement sizing |
| NGFW / threat protection | Configuration and security-profile dependent; current Fortinet model pages should be used for final sizing |
| VPN | IPsec VPN supported; capacity depends on encryption and traffic profile |
| 25GE interfaces | 4 x 25GE/10GE SFP28/SFP+ ultra-low-latency slots |
| 10GE interfaces | 4 x 10GE/GE SFP+/SFP slots |
| GE fibre | 8 x GE SFP slots |
| GE copper | 16 x GE RJ45 data ports |
| Management | 1 x GE RJ45 management port, USB and console interfaces |
| High availability | 1 x 2.5/1GE RJ45 HA port plus FortiOS HA capabilities |
| Security processors | NP7 network processor and CP9 content processor |
| Hardware security | Trusted Platform Module (TPM) |
| Form factor | 1RU rack-mount appliance |
| Power | Dual AC PSU on FG-900G; DC variants are available in the 900G series and must be ordered as the correct model |
| Storage | Base FG-900G and storage-equipped 901G are distinct models; confirm logging/storage requirements before ordering |
The interface ledger is often more important than a single throughput number. A buyer may need four 25GE uplinks for core or aggregation connectivity while still using GE fibre for legacy infrastructure and copper ports for service networks. Matching the port count is only the first step: every optical connection also needs the right transceiver type, fibre mode and connector standard. High-availability designs should duplicate critical interfaces on both appliances and confirm switch-side redundancy.
Performance figures also require context. Pure firewall throughput is not the same workload as intrusion prevention, application control, anti-malware inspection or TLS/SSL inspection. A network that turns on several security profiles for most outbound and inbound traffic should be sized around the inspected workload, peak sessions and future growth rather than the highest published figure. FourTeck can use these inputs to help determine whether the FG-900G is appropriately sized or whether another FortiGate model is a better fit.
Five questions to answer before requesting a quote
01 — What traffic must be protected?
Define internet edge traffic, private WAN, inter-VLAN flows, data-centre server traffic and site-to-site VPN. A design that inspects only north-south internet traffic has different capacity needs from a firewall that also segments large internal server or campus zones.
02 — What is the real peak and growth target?
List current circuit speeds, expected upgrades, peak concurrent users, application mix and the proportion of encrypted traffic. Add reasonable growth for new sites, cloud connectivity and heavier SaaS use. This protects the project from choosing a model that fits today but is undersized after the next network upgrade.
03 — Which existing systems must connect?
Confirm core-switch speeds, transceiver families, dynamic routing protocols, VLAN design, authentication sources, logging platforms, monitoring tools and any existing Fortinet Security Fabric components. Compatibility is not simply a port-count question; it includes software, routing and operational processes.
04 — Which services and support term are required?
FortiGuard bundle selection affects the security capabilities and renewal plan. FortiCare support also has different service levels and terms. Procurement should decide whether the organisation wants a one-, three- or five-year commercial horizon and which security services are required by policy.
05 — What resilience and deployment expectations apply?
Clarify whether the firewall will run as a standalone appliance or HA pair, which power source is available, whether AC or DC hardware is required, rack space, airflow, maintenance windows, implementation responsibility and preferred delivery coordination.
Quote Preparation
Share expected inspected throughput, internet/WAN speeds, number of sites, VPN demand, high-availability requirement, preferred support term, FortiGuard bundle, AC/DC power, transceiver needs, rack environment and project quantity.
Where this class of firewall is most useful
Enterprise internet edge
A large head office or central campus may aggregate substantial internet traffic and require application control, intrusion prevention, malware inspection, VPN and policy-based routing at the same edge. The 900G’s high-speed interfaces and security processing make it a candidate when 10GE or 25GE connectivity is part of the design. Sizing should be based on the security profiles that will actually be enabled.
Data-centre perimeter and segmentation
Organisations can place the appliance between internet-facing services, partner networks, server zones or cloud connectivity paths where policy must be enforced at high throughput. Designers should calculate east-west as well as north-south traffic if the appliance will inspect internal data-centre flows.
Multi-site secure SD-WAN hub
A headquarters or hub site may terminate many branch tunnels and use SD-WAN policy to steer traffic across several carriers. The platform can consolidate routing and security policy, but the number of tunnels, encrypted throughput, routing scale and branch growth must be included in the design.
Large campus security core
Universities, government environments and large institutions may need policy enforcement between administrative, staff, student, guest, server and service networks. The physical interface range supports different aggregation methods, while segmentation rules can limit unnecessary lateral communication.
Hardware acceleration matters most when policy becomes complex
Enterprise firewalls are asked to do more than allow or deny traffic. They identify applications, evaluate sessions against intrusion-prevention signatures, inspect files, apply web and DNS policy, terminate encrypted VPNs and frequently inspect encrypted internet traffic. Each additional security function consumes resources. Fortinet addresses this by using purpose-built security processors in the 900G platform, including the NP7 for network processing and CP9 for content processing.
The buyer benefit is not that hardware acceleration removes the need for capacity planning; it gives the platform a specialised architecture for workloads common to network security. Actual performance still depends on packet size, session mix, policy configuration, security profiles and software version. That is why procurement teams should not use one headline throughput number as a guarantee for every deployment.
For a project, define a realistic traffic model. Estimate how much traffic will pass through full security inspection, how much is site-to-site VPN, how many internet sessions are expected during peak periods, and whether internal segmentation will add traffic that never touches the WAN. This workload model makes it easier to select a firewall with enough headroom for both present demand and the next bandwidth upgrade.
25GE, 10GE, fibre and copper in one appliance
The physical design supports a broad mix of enterprise connection types. Four 25GE/10GE SFP28/SFP+ ultra-low-latency slots can serve high-speed uplinks, four additional 10GE/GE SFP+/SFP slots provide flexible core or aggregation links, eight GE SFP slots support lower-speed fibre, and sixteen GE RJ45 ports cover copper-connected networks. A dedicated management port and a 2.5/1GE HA port separate administrative and resilience functions from ordinary data interfaces.
A firewall quote should therefore include more than the chassis. The complete bill of materials may need SFP/SFP+/SFP28 transceivers, fibre patch leads, direct-attach cables, rack accessories and redundant upstream switch connectivity. Missing these items can delay an otherwise correct appliance purchase.
Subscription design is part of the firewall architecture
The appliance provides the hardware platform and FortiOS, while many advanced threat-prevention capabilities depend on the chosen FortiGuard security services. Different commercial bundles package services in different ways, and FortiCare support is also part of the procurement decision. A security team should identify which controls are mandatory—such as intrusion prevention, malware protection, web or DNS filtering, application control and other enterprise services—then select the bundle that supports the organisation’s policy.
Term length also changes lifecycle planning. A one-year purchase can lower the initial commitment but creates an earlier renewal event. Longer terms can align with a multi-year security programme, though budgets, technology refresh cycles and contract policy differ between organisations. There is no universal best term.
Buyer decision checklist
- Which FortiGuard services are required by security policy?
- Which FortiCare support level is required by the organisation?
- Should the quote cover one, three or five years?
- Will the firewall participate in centralised management or analytics?
- Are ZTNA, SD-WAN and VPN functions part of the first deployment phase?
- Who owns renewal tracking and configuration maintenance?
FourTeck can help map these answers to a current commercial bundle rather than assuming the base appliance alone represents the full production requirement.
What buyers should check before purchase
| Risk | What to confirm | Why it matters | What to share with FourTeck |
|---|---|---|---|
| Wrong capacity assumption | Inspected throughput, sessions and VPN | Security services reduce the relevance of raw firewall throughput | WAN speeds, policy set, encryption mix and growth |
| Incomplete bill of materials | Optics, cables, rack, redundant links | A chassis cannot connect to fibre infrastructure without correct transceivers | Switch models, fibre type, link distance and port speeds |
| Wrong subscription | FortiGuard bundle and FortiCare term | Security features and lifecycle costs depend on these choices | Required controls, support level and contract term |
| Resilience mismatch | Standalone vs HA, AC vs DC, dual feeds | Availability design depends on matched hardware and infrastructure | Rack power, HA topology and maintenance expectations |
The largest purchasing risk is often not choosing the wrong brand or even the wrong family; it is specifying the correct appliance without the supporting components and services required for production. A technically capable firewall can still become a poor deployment if its optics do not match the core switches, if a renewal bundle is omitted, or if an HA design lacks independent power and upstream paths. Treat the purchase as a small infrastructure project rather than a single SKU.
Procurement support for Uganda projects
FourTeck can assist Uganda organisations with model selection, configuration review, quote preparation and delivery coordination for the Fortinet 900G series. Availability can vary by appliance variant, subscription term, optics and project quantity, so an enquiry should specify whether the requirement is for the base FG-900G, an HA pair, an AC or DC design, and which FortiGuard and FortiCare services are expected. For Kampala projects, sharing the deployment timeline and technical bill of materials early helps the quotation process focus on the actual production design rather than only the chassis. Warranty and support guidance should be confirmed against the selected FortiCare service and supply route at the time of quotation.
Uganda project coverage
FourTeck can coordinate enquiries for customers in Kampala and support project discussions for organisations operating in Entebbe, Jinja, Mbarara and Gulu. The practical requirement is to provide the destination, quantity, configuration and target deployment window so delivery planning can be reviewed as part of the quote. This coverage statement does not imply local stock in every city; availability depends on the selected model, service bundle and supply schedule.
East Africa and regional procurement coordination
Organisations planning a standard Fortinet firewall architecture across more than one country may need consistent product families, license terms and support expectations. FourTeck can discuss requirements originating in Uganda and coordinate related enquiries for Kenya and selected East Africa or wider Africa markets where appropriate. Regional project planning is most effective when the customer provides a common technical standard, expected quantities by country and deployment phases. For separate regional enquiries, buyers can also review FourTeck Kenya, FourTeck Africa, FourTeck UAE and FourTeck Kuwait. Branch presence, stock position, warranty handling and delivery times should always be confirmed for the specific country and order.
Related Fortinet paths to consider
Browse FourTeck Uganda business IT solutions or send the project requirements to FourTeck for a model comparison tied to your actual traffic and security needs.
Practical help between the requirement and the purchase order
01. Product selection guidance helps compare the requested appliance against the real workload rather than assuming that an existing model number is automatically correct.
02. Configuration review can identify missing transceivers, HA requirements, power variants, support terms and subscription choices before the quote is finalised.
03. Quote assistance gives procurement teams a clearer bill of materials that can be evaluated against the intended deployment and project quantity.
04. Business IT understanding matters when a firewall purchase interacts with switching, fibre, rack power, WAN circuits, routing and authentication systems.
05. Uganda delivery coordination can be discussed after the destination, configuration and supply requirements are defined.
06. Alternative product matching can be useful when the requested model is oversized, undersized or unavailable for the required project timeframe.
FortiGate 900G buyer questions
01. What is the FortiGate 900G primarily used for?
It is an enterprise next-generation firewall for high-capacity perimeter security, secure SD-WAN, segmentation, VPN and application-aware inspection. It is most relevant where an organisation needs significantly more throughput and interface flexibility than branch-class appliances. The final design should still be based on inspected traffic and enabled security services, not only the raw firewall rating.
02. Does the FG-900G support 25 Gigabit Ethernet?
Yes. Fortinet lists four 25GE/10GE SFP28/SFP+ ultra-low-latency slots on the FG-900G. It also includes four 10GE/GE SFP+/SFP slots, eight GE SFP slots and sixteen GE RJ45 data ports. The required optics or cables are separate design items and should be checked for compatibility with the connected switches and fibre infrastructure.
03. Is FortiGuard licensing required?
The appliance can be purchased as hardware, but many advanced threat-prevention services depend on FortiGuard subscriptions, and FortiCare provides support services. Buyers should define which security controls are required and choose an appropriate bundle and term. A production quote should therefore distinguish the chassis from the services needed for the intended security policy.
04. Can the 900G be deployed as a high-availability pair?
Yes, FortiOS supports high-availability designs and the appliance includes a dedicated 2.5/1GE HA port. A resilient deployment normally requires two correctly matched appliances plus redundant upstream and downstream connectivity, power planning and tested failover procedures. The complete HA bill of materials should be designed before ordering rather than adding a second unit later without infrastructure review.
05. What is the difference between FG-900G and FG-901G?
They belong to the same 900G series, but the storage configuration differs. Buyers that need local logging or storage-related functions should verify whether the storage-equipped 901G is appropriate. The base FG-900G should not be assumed to have the same internal storage configuration. FourTeck can help confirm the exact appliance part number during the quote stage.
06. How should we size the firewall for SSL inspection?
Use the vendor’s SSL inspection and threat-protection test figures together with your real encrypted traffic mix, security profiles and growth expectations. SSL inspection is a materially different workload from basic firewall forwarding. For a conservative design, estimate the percentage of traffic that will be decrypted and inspected, then maintain capacity headroom for peaks and future bandwidth upgrades.
07. What information should we provide for a Uganda quote?
Provide the number of appliances, required HA design, WAN and core-link speeds, expected inspected traffic, VPN requirements, FortiGuard bundle, FortiCare term, AC or DC power preference, optics, installation destination and target deployment date. These details let the quotation address the complete project rather than only the firewall chassis.
08. Can it work as a secure SD-WAN hub?
Yes. FortiOS includes secure SD-WAN capabilities, and the platform can be considered for a central hub that terminates multiple WAN and VPN paths. The design should account for encrypted throughput, number of branches, routing scale, application steering rules and high-availability requirements. Central management may also be useful in larger multi-site environments.
09. Are transceivers included with the firewall?
Do not assume that every required SFP, SFP+ or SFP28 optic is included. Transceivers are typically selected according to link speed, fibre type, distance and the connected equipment. Include the exact optics, direct-attach cables or fibre patching in the bill of materials and verify supported modules before installation.
Build the quote around your network, not just the model number
Send FourTeck your expected inspected throughput, uplink speeds, HA requirement, FortiGuard services, support term, power preference and optic requirements. The team can use those details to prepare a configuration-focused Uganda quotation and flag related components that may be needed for deployment.


Reviews
There are no reviews yet.