
Fortinet FortiNDR 3600G Centralized Network Detection and Response Center
Fortinet FortiNDR 3600G is a high-capacity, on-premises center appliance for organizations that want centralized visibility, investigation and operational control across distributed FortiNDR sensors. Rather than acting as a standalone traffic sensor, the 3600G is designed specifically for center mode. That distinction matters during procurement: the appliance should be treated as the central coordination and investigation layer of a broader FortiNDR architecture, with physical or virtual sensors selected separately for the locations and network segments where traffic is observed.
For Ugandan enterprises, the model is particularly relevant where security teams operate multiple sites, data centers, campus networks, branch environments or segmented operational networks and need to bring detection findings into one controlled on-premises platform. Centralization can reduce the operational friction created when analysts must work across isolated tools, disconnected sensor consoles and inconsistent retention policies. The 3600G provides a purpose-built foundation for a more coordinated detection and investigation workflow while supporting environments that have data-residency, air-gap or local-control requirements.
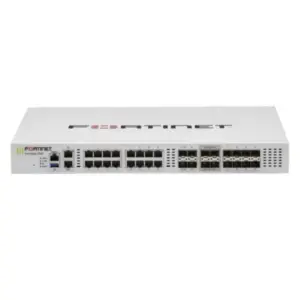
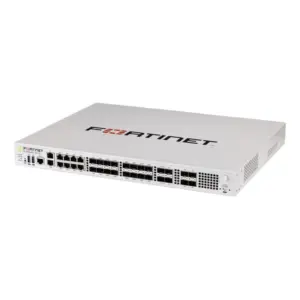
The appliance is supplied with twelve hot-swappable drives fully populated, four 10GbE SFP+ interfaces, a 1GbE RJ45 interface, console connectivity and 1+1 redundant power input. Fortinet’s current ordering guidance identifies the model as center-only and indicates management of up to 50 sensors, while its deployment documentation describes large local storage intended for extended event and analysis retention. These characteristics make correct sizing important: sensor count, traffic profile, retention objectives, uplink design, licensing and high-availability requirements should be established before the final bill of materials is approved.
FourTeck supports procurement teams with configuration validation, quote preparation, accessory checks, licensing alignment and deployment planning. A useful request should include the number of sites, expected sensor count, approximate monitored traffic, preferred retention period, rack location, power arrangement, required support term and whether a secondary center is planned for resilience.
Instant Specifications & Procurement Fact Rail
FNR-3600G
Center mode only
Up to 50 sensors
4 × 10GbE SFP+
12 hot-swappable drives
1+1 redundant input
Procurement status, lead time, warranty entitlement and support duration should be confirmed on the issued quotation because these can vary by order date, selected bundle and service term. Transceivers should also be treated as a separate bill-of-materials item unless the quotation explicitly includes them. For multi-site projects, identify the exact sensor models and quantities because the 3600G itself is the center rather than the packet-observation endpoint.
Operational Product Architecture & Overview
The FortiNDR architecture separates distributed observation from centralized investigation. Sensors are positioned where network activity can be observed, while the 3600G operates as the center that connects those sensor deployments into a common operational view. This design is useful for organizations with many network zones because it avoids forcing every monitored location into one physical capture point. A headquarters, secondary data center, branch aggregation layer, campus core or operational technology zone can use an appropriately sized sensor while the central team works from the center platform.
Center mode changes how the appliance should be evaluated. Buyers should not compare the 3600G with a conventional firewall by counting protected interfaces or expecting it to sit inline as a traffic enforcement gateway. Its value is in centralized investigation, retention and management. That means the design conversation starts with monitored locations, sensor connectivity and operational workflows rather than WAN throughput alone. Network teams should map SPAN, TAP or virtual traffic visibility at the sensor layer, while security architects define how those sensors communicate with the center and how administrators reach the management plane.
The hardware platform supports four 10GbE SFP+ interfaces and redundant power, with substantial local storage. Fortinet deployment guidance describes approximately 176 TB usable storage for the 3600G in a RAID 5 arrangement and gives an illustrative retention figure of up to 365 days in an average 10Gbps test scenario. Actual retention is workload dependent. Event density, file-analysis volume, network throughput, traffic composition and configured retention settings all affect consumption. Procurement teams should therefore treat published retention figures as planning references rather than unconditional guarantees.
A recurring operational pain point is fragmented investigation. An analyst may see one event in a branch, another at headquarters and a third inside a data-center segment, yet lack a convenient way to correlate the broader pattern. A center architecture is intended to improve that operational picture. Another pain point is data governance. Organizations in regulated or sensitive sectors may prefer on-premises storage and locally controlled infrastructure. FortiNDR’s on-premises model supports such requirements and can also be planned for restricted-connectivity environments, although update procedures must be incorporated into operating processes.
Capacity planning should account for growth. A deployment that starts with ten sensors may expand as new branches, server zones or campus segments are brought under observation. Fortinet’s ordering information indicates that the 3600G can manage up to 50 sensors, giving architects room to build a phased rollout. The limit should still be considered together with traffic characteristics and operational retention goals. The correct design is not simply the maximum number of sensors; it is the combination of sensor quantity, sensor performance, data generated, retention policy and analyst workflow.
High availability is another architectural consideration. Fortinet describes dual-center support for the 3600G. Organizations with strict continuity requirements should determine whether a secondary center is needed, where it will be located, how power and network dependencies will be separated, and how operational procedures will handle maintenance or an outage. These decisions should be made during solution design rather than after the first appliance is installed.
Enterprise Business Outcomes & Value Analysis
Key Hardware & Software Highlights
Center-Only Architecture
Purpose-built for centralized FortiNDR management and global investigation. Physical or virtual sensors are purchased and deployed separately according to traffic and site requirements.
Large Local Storage
Twelve hot-swappable drives provide a high-capacity local storage foundation. Retention must be sized against traffic, event volume and file-analysis behavior rather than assumed from raw capacity alone.
10GbE Connectivity
Four 10GbE SFP+ interfaces support high-speed center connectivity. Optics or compatible copper transceivers should be explicitly included in the accessory plan when required.
Redundant Power
1+1 redundant power input supports resilient rack designs when connected to independent power sources. The surrounding UPS and PDU design remains part of the customer’s infrastructure plan.
Dual-Center Support
Organizations with stringent continuity objectives can design a two-center architecture. Site separation, routing, administration and recovery procedures should be documented during implementation planning.
On-Premises Control
The platform is suitable for organizations that require locally hosted detection infrastructure, including environments with restricted connectivity or strong data-governance requirements.
Technical Specifications Ledger
| Item | FortiNDR 3600G Detail | Procurement Note |
|---|---|---|
| Product code | FNR-3600G | Use the exact code on quote and purchase order. |
| Operating mode | Center only | Requires separately selected physical or virtual sensors. |
| Managed sensors | Up to 50 | Plan current and future site count. |
| SFP+ interfaces | 4 × 10GbE SFP+ | Transceivers are normally ordered separately. |
| RJ45 | 1 × 1GbE RJ45 listed in appliance order information | Confirm intended port function against current deployment guide. |
| Console | 1 × RJ45 console | Useful for local administration and recovery workflows. |
| Drives | 12 hot-swappable drives, fully populated | Provides large local event and analysis capacity. |
| Usable storage | Approximately 176 TB in Fortinet deployment guidance | Actual retention depends on workload and configured policies. |
| RAID | RAID 5 referenced for center storage | Validate current shipping configuration at order time. |
| Retention guidance | Up to 365 days in Fortinet’s illustrative 10Gbps planning scenario | Not a fixed guarantee; traffic composition changes results. |
| Power | 1+1 redundant power input | Connect to independent feeds where resilience is required. |
| High availability | Dual-center support | A second center and associated services may be required. |
Physical dimensions, input voltage, maximum power draw, acoustic characteristics, operating temperature and compliance markings should be verified against the current Fortinet hardware documentation and quotation before data-center approval. These values can be critical to rack engineering and should not be inferred from other FortiNDR models. FourTeck can include those checks in bill-of-materials validation.
Configuration & Sizing Worksheet
Step 1 — Estimate Workload and Scale
List every location and network zone that requires observation. Record peak and typical traffic, critical applications, east-west traffic requirements and whether the site is physical, virtual or cloud-hosted. Then map each location to an appropriate FortiNDR sensor. The 3600G can manage up to 50 sensors, but sensor count alone is not a complete sizing metric. Traffic composition and retention needs determine the volume of information that ultimately reaches the operational platform.
Step 2 — Define Retention
Decide how long investigators need access to historical events and analysis records. Regulatory policy, incident-response procedures and internal audit needs may all influence the target. Fortinet provides a 365-day illustrative figure for the 3600G in a tested average 10Gbps scenario, but actual retention varies. Build a margin into the plan rather than designing around an idealized maximum.
Step 3 — Validate Rack, Power and Cabling
Reserve suitable rack capacity, confirm front-to-rear service clearance, verify cooling and map both redundant power inputs to appropriate PDUs. Where continuity is important, each supply should terminate on an independent protected feed. Confirm whether 10GbE connectivity will use fiber optics, direct-attach cabling or an approved copper SFP+ option. Do not assume optics are bundled with the base appliance.
Step 4 — Select Services and Subscriptions
Review the selected FortiCare and FortiNDR service bundle carefully. Fortinet publishes multiple hardware and service combinations, and some capabilities such as NetFlow support may be licensed separately. The commercial quote should identify hardware, support term, update services and any optional service lines individually enough for the buyer to understand renewal obligations.
Step 5 — Prepare the Quote Package
For a precise quote, provide the FNR-3600G requirement, desired support duration, number and model of sensors, transceiver types and quantities, redundancy requirements, deployment locations, target delivery date and whether staging or pre-configuration is required. Include any procurement rules that require serial-number recording, manufacturer authorization, tax documentation or specific warranty language.
Deployment Scenarios & Industry Use Cases
Large Enterprise and Multi-Site Networks
A large enterprise can place sensors at headquarters, data centers and high-value branches while using the 3600G as the central investigation point. This approach is suitable where network teams already have distributed switching and routing domains and want security observation to follow that topology. A phased rollout can begin with critical sites and expand toward the platform’s sensor-management ceiling. The architecture should include secure management paths, consistent time synchronization, defined sensor naming and documented retention policies.
Financial and Banking Institutions
Banks and financial organizations often need strong visibility across data-center segments, digital service infrastructure, branch networks and administrative systems. An on-premises center can support governance requirements where security data must remain under direct organizational control. Procurement teams should plan dual-center resilience for high-criticality environments, segregate management access, document change control and align retention with internal risk and regulatory policies. Sensor placement should prioritize transaction-supporting infrastructure and high-value east-west traffic.
Educational and Campus Networks
Universities and large educational institutions operate highly diverse environments that may include student networks, staff systems, research infrastructure, data centers, wireless services and public-facing applications. Distributed sensors can help security teams observe key segments without treating the campus as one homogeneous network. Central investigation supports a small security team that needs to work across multiple buildings and logical zones. Capacity planning should account for seasonal peaks, large file transfers and research workloads.
Government and Defense Procurement
Public-sector and restricted environments may prioritize on-premises data control, segmented networks and controlled update processes. FortiNDR supports on-premises operation and Fortinet documents procedures for offline update scenarios. Deployment planning should identify which networks can reach update services, which must remain isolated, how update media or procedures are controlled, and how administrative access is audited. For sensitive projects, the final architecture should be validated against agency security policy before installation.
Technical Deep Dive 1: Processing, Acceleration & Center Architecture
The 3600G should be understood through the division of responsibilities between sensors and center. Sensors observe network activity at distributed points, while the center aggregates operational visibility and supports global investigation. This separation is important because it lets network observation remain close to the traffic source. A branch or data-center sensor can be selected according to local throughput rather than backhauling all monitored traffic to one central appliance.
From an engineering perspective, this also changes uplink planning. The center requires reliable connectivity to its managed sensors and to administrative systems, but the design objective is not to create a new inline choke point for production traffic. The four 10GbE SFP+ interfaces provide high-speed connectivity for the center platform, while sensor-side interfaces and traffic capture are sized independently. This modularity is valuable when organizations have different network speeds at different sites.
Storage is a major part of the center architecture. Fortinet’s deployment guidance describes approximately 176 TB usable capacity and an illustrative 365-day retention figure under an average 10Gbps scenario. Retention settings should be actively managed because physical disk exhaustion can affect processing. Teams should monitor capacity trends and adjust policy before limits are reached. Historical visibility is useful only when retention is sustainable under real traffic conditions.
Technical Deep Dive 2: Software Ecosystem, Firmware Security & Operational Control
FortiNDR operates as part of Fortinet’s broader security ecosystem and can integrate with local Fortinet Security Fabric components. This matters for organizations already operating FortiGate and other Fortinet technologies because operational processes can be designed around an established vendor ecosystem rather than adding an entirely disconnected detection platform. Integration design should still be documented explicitly: define what information is exchanged, which systems initiate actions, which administrators own each component and how changes are approved.
Fortinet’s administration guidance calls for stable internet access for FortiGuard updates in normal deployments and also provides procedures for offline environments. Organizations with proxies, restricted outbound access or isolated networks should resolve the update method before commissioning. Firmware and service updates should be governed through change windows, backups and rollback planning. Production security infrastructure should not be updated ad hoc simply because a newer release is available.
Administrative security deserves equal attention. Place the management interface on a controlled network, restrict access to approved operator workstations, apply strong authentication policy, synchronize time and send relevant administrative records to the organization’s logging platform. Where a secondary center is deployed, operational teams should document how configuration consistency and failover responsibilities are maintained.
Technical Deep Dive 3: High Availability, Redundancy & Disaster Recovery
The appliance includes redundant power input and Fortinet’s ordering guidance describes dual-center support. These features provide building blocks for resilience, but availability depends on the entire system design. Two power supplies connected to the same PDU do not protect against a PDU failure. Two centers installed in the same rack do not protect against a room-level outage. Resilience therefore begins with failure-domain analysis.
For critical deployments, place redundant power feeds on separate protected circuits, use resilient upstream switching and consider geographically separated centers where operational policy requires it. Define the expected behavior when a center is unavailable, the process for restoring service, and the personnel authorized to perform recovery actions. Disaster recovery documentation should include management addressing, DNS and time dependencies, certificate or credential requirements, sensor reconnection procedures and configuration backup locations.
Routine testing is essential. A high-availability design that has never been exercised remains an assumption. Schedule controlled tests to verify power-feed independence, administrative access, sensor behavior and recovery procedures. Record observed recovery times and update runbooks when the environment changes. This operational discipline turns redundant hardware into a dependable service design.
Pre-Purchase Buyer Gap Checklist
Are sensors included? No assumption should be made that the center appliance includes all required sensors. Fortinet identifies the 3600G as center-only, so physical or virtual sensors must be selected for the monitored locations.
Are transceivers included? Fortinet’s documentation indicates transceivers are purchased separately. The quote should therefore specify SFP+ optics, DACs or approved copper transceivers where required.
Are there additional service costs? Hardware and service bundles vary, and some capabilities can be licensed separately. Request a line-by-line commercial schedule showing the base appliance, support, update services, optional services and renewal terms.
Is 365-day retention guaranteed? No. The figure is a planning reference based on a tested average traffic scenario. Real retention depends on throughput, traffic mix, event density and configured settings. Use measured network data when possible.
Can the appliance work alone? Its intended role is center mode. A functional distributed deployment requires compatible sensors to observe the networks of interest.
How many sensors can it manage? Current Fortinet ordering guidance states up to 50. Plan for both initial deployment and growth so the design does not consume all available scale on day one.
What should be checked in the rack? Confirm physical dimensions, rail requirements, service clearance, airflow, PDU outlets, voltage, UPS capacity and heat load using the current hardware guide before installation.
What about cross-vendor environments? Network observation can exist in heterogeneous infrastructure, but integrations and automated response workflows should be validated individually. Do not assume every third-party platform supports the same depth of integration.
What happens in an isolated network? Fortinet documents offline update approaches. Include the update workflow in security operating procedures and ensure the organization can maintain signatures and platform software without violating isolation requirements.
Uganda Regional Procurement & Delivery Logistics
Enterprise security infrastructure should be quoted as a complete solution rather than a single chassis. FourTeck’s Uganda procurement workflow can begin with a requirements review covering the 3600G center, sensor estate, support duration, service subscriptions, optics, rack accessories and resilience objectives. Once the configuration is validated, the commercial quotation can identify the principal hardware and associated service lines so procurement teams can compare the order against the approved design.
Lead time depends on stock position, distributor allocation, selected service bundle and international logistics at the time of order. Buyers should request a current delivery estimate rather than relying on a generic timeline. For projects tied to data-center migrations, audits or fiscal-year deadlines, include the required-on-site date in the request so sourcing can be planned around that milestone.
Pre-configuration support can include review of management addressing, interface plans, sensor naming, rack placement, software version strategy and deployment documentation. The degree of staging should be agreed before shipment. Where customer policy requires factory-sealed delivery, staging can instead be performed on site. Warranty and support processing should retain serial numbers, purchase documentation and service entitlement records so future cases can be opened efficiently.
Local Coverage Matrix
Kampala
Support for enterprise headquarters, data centers, financial institutions and public-sector procurement.
Entebbe
Project supply for institutional, logistics, hospitality and distributed enterprise environments.
Jinja
Procurement planning for industrial, commercial and multi-site network deployments.
Mbarara
Regional delivery planning for education, healthcare, enterprise and branch infrastructure.
Gulu
Support for regional organizations requiring centralized security visibility across distributed sites.
Delivery scope, on-site services and travel requirements should be confirmed for each project location. Multi-city deployments benefit from a site schedule that identifies local contacts, rack readiness, network prerequisites and acceptance criteria before equipment is dispatched.
Cross-Border & Regional Supply Chains
Organizations operating across East Africa, the Gulf and wider African markets can coordinate Fortinet procurement through FourTeck’s regional channels. Uganda requirements can be initiated through FourTeck Uganda, while Kenyan projects can use FourTeck Kenya. Wider continental requirements can be coordinated through FourTeck Africa. UAE procurement is supported through FourTeck UAE, and Kuwait requirements through FourTeck Kuwait.
For cross-border projects, keep the technical bill of materials consistent while allowing commercial documents, taxes, delivery terms and service logistics to reflect each destination. Central architecture governance helps avoid a situation in which different country teams order incompatible sensors, support terms or optics for the same regional deployment.
Related Products & Internal Planning Paths
A FortiNDR 3600G project normally includes more than the center appliance. Buyers should review compatible FortiNDR sensor models for physical sites, virtual sensor options for supported hypervisors or cloud environments, approved 10GbE transceivers, redundant switching, protected rack power and the appropriate FortiCare and detection service bundles. For a coordinated quotation, start from the Uganda enterprise technology catalog and use the project contact page to submit the complete requirement.
Where a deployment spans multiple countries, compare the Kenya supply channel, Africa regional channel, UAE channel and Kuwait channel. The engineering objective should remain one validated architecture with locally appropriate commercial fulfillment.
FourTeck Technical Service Capabilities
FourTeck can support engineering validation before purchase by reviewing the proposed center-and-sensor topology, sensor quantities, network speeds, retention objectives, interface requirements and resilience strategy. This stage is intended to catch design gaps before they become purchase-order problems. Bill-of-materials verification can also identify omitted optics, service subscriptions, support terms or accessories.
For projects that permit staging, pre-shipment preparation can include agreed firmware review, management addressing plans, inventory documentation and configuration checklists. Where customer security policy requires untouched factory packaging, the same preparation can be delivered as an implementation plan for on-site execution. Firmware updates should always follow the customer’s change-control policy and compatibility requirements.
Post-sales support can assist with entitlement verification, hardware support cases, replacement coordination and configuration troubleshooting within the agreed service scope. For critical infrastructure, buyers should define response expectations, escalation contacts and vendor support coverage before commissioning so incident procedures are clear when an issue occurs.
Extended Technical FAQ
1. What is the FortiNDR 3600G primarily used for?
The FortiNDR 3600G is primarily a center appliance for centralized FortiNDR management and investigation. It is not positioned as a standalone sensor for directly observing every target network. In a typical design, compatible physical or virtual sensors are deployed where network traffic needs to be monitored, and those sensors are connected operationally to the 3600G center. This makes the appliance suitable for large distributed environments in which a central security team needs a consolidated view across many sites or network zones. Procurement should therefore include both the center and the required sensor estate.
2. How many sensors can the FortiNDR 3600G manage?
Fortinet’s current ordering guidance lists support for up to 50 sensors managed by the 3600G. This provides useful scale for enterprises with multiple branches, campuses, data centers or segmented environments. The best design should not automatically consume the maximum number, however. Architects should allow room for growth and evaluate the data generated by each sensor, retention objectives and operational workflow. A deployment with fewer high-volume sensors can have different storage and investigation characteristics from one with many smaller sites, so the full environment should be sized rather than relying on sensor count alone.
3. Does the appliance include the sensors required for network monitoring?
The 3600G is identified as a center-only model, and physical or virtual sensors should be selected separately. This is one of the most important commercial details to clarify before issuing a purchase order. The quote should state each sensor model, quantity, support term and required accessories. Virtual sensor deployments should also confirm the supported virtualization or cloud platform and allocated resources. Treating the center as one component of a complete architecture helps prevent an incomplete order that cannot provide the planned network visibility after delivery.
4. What storage and retention should buyers expect?
Fortinet deployment guidance describes approximately 176 TB usable storage for the 3600G and provides an illustrative retention period of up to 365 days in an average 10Gbps test scenario. Actual retention is not fixed. Network throughput, event density, traffic composition, file-analysis volume and configured retention settings all affect consumption. Buyers with strict historical-data requirements should use measured traffic data and establish a capacity margin. Operations teams should monitor disk utilization after deployment and adjust retention policies before physical storage limits are approached.
5. Does FortiNDR 3600G support high availability?
Fortinet lists dual-center support for the 3600G and the hardware includes redundant power input. A resilient design may therefore use a second center together with independent power and network paths. High availability should be treated as an architectural project rather than a checkbox. Teams need to decide where each center resides, how failure domains are separated, how sensors behave during a center outage and how administrators restore normal operation. Regular failover testing and documented runbooks are recommended for environments with strict recovery objectives.
6. Are 10GbE transceivers included with the appliance?
Transceivers should be planned as separate items unless the issued quotation explicitly states otherwise. The 3600G provides 10GbE SFP+ connectivity, so the project team should decide whether each connection will use supported optical modules, direct-attach cabling or an approved copper SFP+ transceiver. The correct choice depends on switch interfaces, distance, cabling plant and data-center standards. Omitting optics is a common cause of installation delay, so interface mapping should be completed before the purchase order is finalized.
7. Can FortiNDR 3600G be used in an isolated or air-gapped environment?
FortiNDR is offered as an on-premises platform suitable for environments that require local control, and Fortinet documentation includes guidance for offline update procedures. The operational challenge is maintaining current platform and security-service data without violating isolation requirements. Before deployment, define the approved update workflow, responsible personnel, change windows, media handling if applicable and rollback process. Restricted environments should also plan time synchronization, administrative access and support procedures carefully because normal internet-dependent operational assumptions may not apply.
8. What licensing and support costs should be expected?
Commercial requirements depend on the selected hardware bundle, FortiCare term, detection service coverage and optional services. Fortinet publishes multiple orderable service combinations, and some capabilities such as NetFlow support may be licensed separately. Buyers should request a quotation that separates hardware, support and optional service lines clearly and shows the term for each recurring entitlement. This makes first-year cost and future renewal obligations easier to understand and helps procurement teams compare the proposal with the technical design.
9. What information should be supplied for an accurate Uganda quotation?
Provide the FortiNDR 3600G requirement, number of sites, proposed sensor count, approximate traffic per site, preferred retention period, required support duration, target delivery date, rack location and whether high availability is required. Also identify switch interface types so transceivers can be selected correctly. If the organization already operates Fortinet infrastructure, mention relevant products and software versions because integration planning may influence the final design. For regulated procurement, include any required warranty wording, manufacturer documentation or acceptance criteria at the quotation stage.
10. What happens if a hardware component fails after deployment?
Hardware replacement is governed by the active FortiCare entitlement and the service level purchased. Keep serial numbers, invoices, entitlement records and deployment details accessible to the support team. When a fault occurs, gather diagnostic information without disrupting evidence or production operations, open the appropriate support case and follow the approved replacement workflow. Organizations with strict availability targets should not rely solely on replacement speed; they should design redundancy at the power, network and center level so a single hardware incident does not become an avoidable operational outage.
Plan Your FortiNDR 3600G Deployment in Uganda
A successful FortiNDR 3600G purchase starts with a validated architecture. Confirm the number of monitored locations, physical and virtual sensors, traffic characteristics, retention objective, 10GbE connectivity, support term and resilience requirements before the order is placed. This prevents common procurement gaps such as missing sensors, omitted optics, incomplete service coverage or insufficient rack and power planning.
FourTeck can prepare a project quotation for Kampala, Entebbe, Jinja, Mbarara, Gulu and other Uganda locations, with cross-border coordination available for wider regional deployments. Submit your network scope and target schedule to begin bill-of-materials validation and commercial preparation.

Reviews
There are no reviews yet.